Home Blog Page 7

Georgia Power data breach exposes 400,000 customer accounts

0

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.yahoo.com

Georgia Power detected unauthorized access to its online customer portal, exposing account information belonging to approximately 400,000 customers tied to its parent company, Southern Company, the company said. Of those, 300,000 were Georgia Power customers.

The breach exposed customers’ names, addresses, phone numbers, email addresses, and the last four digits of their Social Security numbers, the company said. Bank account numbers, payment card information, and driver’s license numbers were not accessed, according to CBS News Atlanta.

“We recently detected suspicious activity involving our online customer portal. An unauthorized third party accessed certain, limited information about the accounts of approximately 400K customers,” Georgia Power said in a statement.

The company said it took steps to halt the activity upon detection and contacted law enforcement. Georgia Power said it has since completed an investigation and found no evidence that unauthorized access is continuing. The identity of the third party behind the breach has not been released.

Georgia Power said it is reaching out to affected customers and has arranged complimentary credit monitoring and identity theft restoration services through Equifax for a period of one year. Affected customers received details on how to enroll in the monitoring service within the notification emails Georgia Power sent them.

The company also warned customers to be alert to impersonation attempts. “We will never threaten immediate disconnection or demand payment over the phone,” Georgia Power said. “If you suspect someone is pretending to be a Georgia Power employee, hang up or don’t reply, and call us directly at the number on your bill or our website.”

The breach adds to a surge in data compromises that has accelerated in 2026. The Identity Theft Resource Center tracked 1,803 data compromises in the first half of 2026, putting the year on pace to surpass the record 3,321 incidents recorded across all of 2025. One in four malicious breaches between March 2025 and February 2026 were AI-enabled, a 56% increase over the prior year, according to an IBM study.

Utilities have been among the targets. Georgia was one of multiple states that experienced cyberattacks on water infrastructure last year, according to WSB-TV. U.S. officials have sounded alarms about foreign government-linked hackers ramping up attacks on critical infrastructure such as electric utilities and water systems, according to WSB-TV.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Georgia Power data breach exposes 400,000 customer accounts”,
“datePublished”: “2026-10-06 12:11:00”,
“image”: “https://s.yimg.com/lo/mysterio/api/9c7b98d0ab1e23c587f91070cec081e988e298f9e492d45672ee7669a84950a4/lightyear_networkapi/resizefill_w1200%3Bquality_80%3Bformat_webp/https%3A%2F%2Fmedia.zenfs.com%2Fen%2Fquartz_855%2Fb05734effe5745486740834c0882f8b1.jpg”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.yahoo.com/news/us/articles/georgia-power-data-breach-exposes-121102445.html”,
“mainEntityOfPage”: “https://www.yahoo.com/news/us/articles/georgia-power-data-breach-exposes-121102445.html”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

ARUP Artificial Intelligence Project Selected for Redtail AI Factory Challenge Project

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.morningstar.com

ARUP Artificial Intelligence Project Selected for Redtail AI Factory Challenge Project

SALT LAKE CITY, Oct. 6, 2026 /PRNewswire/ — ARUP Laboratories has been selected for the second cohort of challenge projects in Utah’s Redtail AI Factory with its project, “Scaling EventHorizon with Redtail: A Foundation Model for Clinical Flow Cytometry.”

The award will provide researchers at the ARUP Institute for Research and Innovation in Diagnostic and Precision Medicine (R&I Institute) with access to Redtail, a new statewide artificial intelligence (AI) supercomputing infrastructure managed by the University of Utah. Use of Redtail will enable the team to accelerate development of a proprietary foundation model designed to enhance the analysis of clinical flow cytometry data.

“Redtail gives us access to computational power that can dramatically accelerate innovation,” said Robert Ohgami, MD, PhD, MBA, FCAP, vice president of the ARUP R&I Institute. “What might take months or longer using conventional resources can be accomplished in a fraction of the time, helping us develop AI tools that support pathologists and improve care for patients.”

The project was chosen through a competitive review process that evaluated proposals based on their readiness, innovation potential, anticipated impact, and ability to leverage Redtail’s advanced computing capabilities.

Manish Parashar, U chief AI officer and executive director of the U’s Scientific Computing and Imaging Institute, congratulated ARUP and other Redtail challenge winners who are tackling important research endeavors.

“These teams will serve as pioneers on the Redtail system, paving the way for the rest of the state and demonstrating how advanced AI, enabled by Redtail, can amplify Utah’s expertise, keep us at the forefront of innovation, and deliver real benefits to all Utahns,” he said.

ARUP’s EventHorizon model is being developed by a team made up of David Ng, MD, FCAP, medical director of Hematopathology, Hematologic Flow Cytometry, and Applied Artificial Intelligence and Bioinformatics, and research data scientists Muir Morrison and Mattia Medina Grespan. The tool aims to assist pathologists in analyzing complex flow cytometry data to help diagnose blood cancers and other hematologic diseases.

By training on substantially larger datasets and performing more extensive computational iterations, the model could help identify rare and diagnostically challenging disease patterns that might otherwise be difficult to recognize, Ohgami said. It also has the potential to improve diagnostic accuracy, reduce turnaround times, and help patients receive appropriate therapies sooner.

The Redtail AI Factory recently ranked No. 159 on the Top 500 list of the world’s fastest supercomputers and No. 76 on the Green 500 list for energy efficiency, placing it among the nation’s leading academic AI computing resources, according to the U. Among U.S. public universities, Redtail ranks fifth.

Redtail was created through a $50 million public-private partnership among the U, the state of Utah, Brynn Ballard and Peter Huntsman, and the Huntsman Family Foundation and features state-of-the-art AI infrastructure from Hewlett Packard Enterprise and NVIDIA. The initiative aims to expand access to advanced AI infrastructure for researchers, educators, students, and industry collaborators throughout Utah. More information and a list of other challenge project awards are available on the Redtail website.

About ARUP Laboratories

Founded in 1984, ARUP Laboratories is a leading national reference laboratory and a nonprofit enterprise of the Spencer Fox Eccles School of Medicine at the University of Utah and its Department of Pathology. ARUP offers more than 3,000 tests and test combinations, ranging from routine screening tests to esoteric molecular and genetic assays. In addition, ARUP is a worldwide leader in innovative laboratory research and development, led by the efforts of the ARUP Institute for Research and Innovation in Diagnostic and Precision Medicine. ARUP is ISO 15189 and CAP accredited. For more information, visit www.aruplab.com.

Media Contact

Bonnie Stray
801-583-2787 ext. 2823
[email protected] 

View original content to download multimedia:https://www.prnewswire.com/news-releases/arup-artificial-intelligence-project-selected-for-redtail-ai-factory-challenge-project-302899262.html

SOURCE ARUP Laboratories

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: ” ARUP Artificial Intelligence Project Selected for Redtail AI Factory Challenge Project”,
“datePublished”: “2026-10-06 15:05:00”,
“image”: “https://images.contentstack.io/v3/assets/blt4eb669caa7dc65b2/blta7dd42ebdd7b93b8/61899b34a3c7df383578294c/morningstar-og.png”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.morningstar.com/news/pr-newswire/20261006sf63877/arup-artificial-intelligence-project-selected-for-redtail-ai-factory-challenge-project”,
“mainEntityOfPage”: “https://www.morningstar.com/news/pr-newswire/20261006sf63877/arup-artificial-intelligence-project-selected-for-redtail-ai-factory-challenge-project”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

Cybersecurity jobs available right now: October 6, 2026

0

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.helpnetsecurity.com

Associate IAM Engineer

New York City Office of Technology & Innovation | USA | On-site – View job details

As an Associate IAM Engineer, you will support daily identity and access management operations in Microsoft Entra ID and related platforms. You will manage users, groups, access provisioning, and role assignments, resolve authentication issues and support tickets, and help maintain stable IAM services. You will also document procedures, a

Computer Network Defense Analyst

National Security Agency | USA | On-site – View job details

As a Computer Network Defense Analyst, you will identify vulnerabilities, analyze threats, develop mitigations and cybersecurity products, and educate customers to protect the Defense Industrial Base, critical infrastructure, and U.S. National Security Systems, including NSA systems and networks. You will provide network defense, continuous monitoring, technical analysis, situational awareness, and incident response to protect highly classified systems and data.

Cybersecurity Engagement & Policy Specialist

Commission for Communications Regulation | Ireland | Hybrid – View job details

As a Cybersecurity Engagement & Policy Specialist, you will analyse cybersecurity policy and legislation, develop recommendations for ComReg leadership, and coordinate consultations, workshops, awareness campaigns, and stakeholder events. You will also represent ComReg in national and international forums, monitor emerging risks and stakeholder perspectives, and support cross-divisional cybersecurity projects.

Get weekly updates on new cybersecurity job openings. Subscribe here!

Cybersecurity Engineer

Reyes Holdings | USA | On-site – View job details

As a Cybersecurity Engineer, you will design, implement, and manage security solutions, apply patches and code updates, and investigate incidents to identify root causes and corrective actions. You will collaborate with senior engineers and cross-functional teams to integrate security into operations and maintain technical standards, documentation, runbooks, and playbooks for managed service transitions.

Cybersecurity Technology Architect IV

Astreya | USA | Remote – View job details

As a Cybersecurity Technology Architect IV, you will develop cybersecurity architectures, strategies, and roadmaps that integrate AI, automation, and emerging technologies. You will evaluate tools and integration opportunities, improve interoperability across security domains, and establish controls and guardrails for AI agents and automated workflows.

Cyber Security Developer

BMO | Canada | Hybrid – No longer accepting applications

As a Cyber Security Developer, you will test solutions, troubleshoot defects, and ensure code meets BMO’s security and operational standards. You will also create technical documentation, support implementation with internal teams and vendors, and assist with data validation, audit reporting, and dashboard development.

Must read:
How to succeed at cybersecurity job interviews

Cyber Security Manager

Synopsys | USA | Hybrid – View job details

As a Cyber Security Manager, you will lead a distributed team overseeing security operations, engineering, vulnerability management, incident response, and compliance support for Ansys Government Initiatives. You will manage security technologies, prioritize remediation, coordinate incident response, and document root causes. You will also maintain controls and audit readiness for CMMC Level 2 and other regulatory requirements, partnering with cross-functional teams to integrate security across enterprise systems.

Digital Forensics and Incident Response Analyst

Department of Education | Australia | Hybrid – View job details

As a Digital Forensics and Incident Response Analyst, you will investigate cyberattacks, reconstruct timelines, preserve evidence, and respond to incidents from detection through recovery. You will maintain forensic tools, conduct threat hunting and intelligence analysis, and recommend remediation. You will also collaborate with external response teams and communicate findings through technical and executive reports to strengthen the organisation’s security posture.

Director – Cyber Security

Emirates Global Aluminium | UAE | On-site – View job details

As a Director – Cyber Security, you will lead EGA’s cybersecurity strategy, governance, risk management, compliance, and security oversight across IT and OT environments. You will manage the security team, budgets, policies, training, and stakeholder relationships while protecting enterprise assets and data. You will also guide secure IT and OT integration, maintain network segmentation, and ensure controls support plant safety, system performance, and uninterrupted operations.

Information Security Lead

TCW | USA | Hybrid – No longer accepting applications

As an Information Security Lead, you will lead the security team, turn strategy into daily operations, and report risks and performance to leadership. You will oversee cloud, infrastructure, identity, application, data, and AI security, lead incident response, and manage vulnerability remediation. You will also partner with cross-functional teams to strengthen controls, support financial services compliance, and maintain security standards, playbooks, and governance documentation.

IT Cyber Security Manager

TT-Line | Germany | On-site – View job details

As an IT Cyber Security Manager, you will will implement and maintain the company’s cybersecurity strategy and governance framework, manage risks and vulnerabilities, and coordinate incident response and recovery. You will integrate security into IT and OT initiatives, oversee external testing and audits, and support business continuity and cyber resilience. You will also deliver awareness training and report security performance and risks to executive management.

Principal Security Engineer

Reactor | USA | On-site – View job details

As a Principal Security Engineer, you will define and lead Reactor’s security strategy, protect partner and customer models and data, and address threats across the platform. You will lead security reviews and compliance efforts, represent Reactor within the security and AI community, embed security into development, and establish organization-wide detection and incident response.

Research Cybersecurity Analyst (Information Security Analyst III)

San Diego State University | USA | Hybrid – View job details

As a Research Cybersecurity Analyst (Information Security Analyst III), you will assess and validate security controls across cloud and on-premises research environments, coordinate remediation, and support secure research environments and enclaves.
You will maintain security plans, inventories, procedures, and compliance evidence. You will also support audits, CMMC readiness, vulnerability management, incident readiness, and ongoing compliance.

Senior Network Security Engineer

Compie Technologies | Israel | On-site – View job details

As a Senior Network Security Engineer, you will lead network infrastructure across multiple sites, deploying and maintaining networking and security solutions in on-premises and multicloud environments. You will manage vendor-supported projects, implement new technologies, develop automation, and troubleshoot complex issues to maintain system availability and operational continuity.

Senior Product Security Engineer

Whatfix | India | On-site – View job details

As a Senior Product Security Engineer, you will lead secure development practices, threat modelling, and security reviews for SaaS, cloud-native, and AI/LLM systems. You will test AI security risks, strengthen identity controls, automate security testing, and manage software supply chain risks. You will also develop reusable security patterns, collaborate with engineering teams, mentor junior engineers, and support customer security discussions.

Senior Security Architect

SSE | United Kingdom | Hybrid – View job details

As a Senior Security Architect, you will lead the design and assurance of secure digital, cloud, and data-driven solutions for SSEN Distribution. You will guide threat modelling, govern security controls and reusable architectures, and work with delivery teams to embed security, DevSecOps, and automated testing. You will oversee architectural risks, compliance, and secure operations, ensuring alignment with organisational standards and frameworks such as NCSC, NIST, and IEC 62443.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Cybersecurity jobs available right now: October 6, 2026”,
“datePublished”: “2026-10-06 04:00:00”,
“image”: “https://img.helpnetsecurity.com/wp-content/uploads/2024/03/11140416/cybersecurity_jobs-1-1500.webp”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.helpnetsecurity.com/2026/10/06/cybersecurity-jobs-available-right-now-october-6-2026/”,
“mainEntityOfPage”: “https://www.helpnetsecurity.com/2026/10/06/cybersecurity-jobs-available-right-now-october-6-2026/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

Don’t buy a consultant’s AI framework

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.infoworld.com

Think about what that multiplier means in real money. A monthly inference bill that should be $50,000 becomes $500,000 to $1,000,000. Not because the technology is expensive, but because the architecture was chosen before the requirements were understood, and every downstream decision inherited that mistake.

What you should do instead

Focus on requirements, procedures, and desired outcomes to shape your architecture. Spend the time up front to understand what dynamic behavior the application actually needs, what data it touches, what latency and cost envelopes it must live inside, and what failure looks like.

Work through ideas and concepts honestly, with no vendor intellectual property on the table. When you do this, you’ll spend about one-fourth of the cost to get from idea to development, and the resulting system will cost roughly one-tenth as much to operate each month. Those numbers are not theoretical. They’re what I observe when teams do the architecture work properly, compared with when they start with a framework and backfill.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: ” Don’t buy a consultant’s AI framework”,
“datePublished”: “2026-10-06 09:04:00”,
“image”: “https://www.infoworld.com/wp-content/uploads/2026/10/4230874-0-64884500-1791277487-AI-build-versus-buy-shutterstock_2712621347.jpg?quality=50&strip=all&w=1024”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.infoworld.com/article/4230874/dont-buy-a-consultants-ai-framework.html”,
“mainEntityOfPage”: “https://www.infoworld.com/article/4230874/dont-buy-a-consultants-ai-framework.html”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

Announcing the AWS Digital Sovereignty Lens for the Well-Architected Framework

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: aws.amazon.com

October 2026: This post was reviewed and updated for accuracy.

Today we’re launching the AWS Digital Sovereignty Lens, a new Well-Architected lens providing customers with extended guidance for designing, building, and operating sovereign workloads on AWS.

Customers tell us that digital sovereignty brings a unique set of challenges that existing architecture guidance doesn’t fully address. Sovereignty requirements don’t arrive as a single brief. They come from multiple teams, including privacy, legal, compliance, and security. These requirements sometimes conflict. For example, a localization mandate requires in-country storage, whereas resilience might call for replication across jurisdictions.

Sovereignty also depends on coordinated choices across compute, storage, networking, identity, encryption, and operations. A decision in one layer can weaken a control in another. Third-party dependencies, from software libraries to external APIs, carry jurisdictional exposure of their own.

The lens builds on the AWS Digital Sovereignty Pledge we made in 2022, our commitment to giving you sovereignty controls and features in the cloud without compromising on capabilities, performance, innovation, and scale.

Five questions that define a sovereign workload

The lens treats sovereignty as an architectural concern. It uses five questions to help you determine which concerns apply to your workload and to what degree:

  1. Where is the workload located? (locality)
  2. Who can reach it? (access control)
  3. Will it keep working when conditions change? (continuity)
  4. Can it be transferred elsewhere? (portability and interoperability)
  5. Can you prove sovereignty controls are in place? (transparency and auditability)

The first four concerns can trade off or influence one another. Mandates that restrict technology choices to a narrow pool of providers, for example, can constrain your recovery and exit options. You decide which concern takes precedence, which risks to accept, and why. The fifth question plays a different role. It asks what controls and evidence demonstrate that the other four concerns are addressed.

What’s in the lens

If you’ve run a Well-Architected review the structure is familiar: pillars, questions, and best practices. The lens covers four of the six pillars, with 21 questions and 37 best practices:

  • The operational excellence pillar covers sovereignty governance, compliance automation, continuous auditability, compliance monitoring and remediation, and regulatory change. It answers the fifth question (of the Five questions that define a sovereign workload): can you prove sovereignty controls are in place?
  • The security pillar covers secure foundations, access control, control verification, threat detection, operator access, data protection, and event response. It answers the first two questions: where is the workload located, and who can reach it?
  • The reliability pillar covers continuity planning, third-party risk, portability and interoperability, and disruptions beyond technical failures. It answers questions three and four: will it keep working, and can it be transferred?
  • The performance efficiency pillar covers sovereign deployment choices and software-dependency assessment, weighing all five questions against each other.

For the remaining two pillars, cost optimization and sustainability, the existing Well-Architected guidance applies to sovereign workloads.

What are sovereignty controls?

Sovereignty controls build on capabilities that builders already use, including service control policies (SCPs), resource control policies (RCPs), AWS Identity and Access Management (IAM) policies, firewall rules, and backup policies. No single control meets data residency, data sovereignty, or continuity requirements on its own. They layer together in a defense-in-depth approach. AWS Control Tower groups these controls under its digital sovereignty category, covering data residency, granular access restriction, encryption, and resiliency.

The lens also covers controls you build yourself. These include validating infrastructure templates with AWS CloudFormation Guard, verifying access policies with IAM Access Analyzer, and detecting configuration drift with AWS Config.

Not every sovereignty control is technical. Deciding which personnel can provide operational support, from which locations, and under what authority is an operational control. Reviewing that access on a regular schedule is another. Together, technical and operational controls combine to produce continuous evidence of your sovereignty posture.

This is what sovereign-by-design means in practice. AWS builds sovereignty foundations, such as the Nitro System, which enforces access restrictions so that nobody, including AWS employees, can access customer data running in Amazon Elastic Compute Cloud (Amazon EC2). Your controls express jurisdictional requirements on top of those foundations, using familiar policy tools reinforced by operational controls.

Where sovereignty requirements arise

Sovereignty requirements extend beyond public sector workloads. The lens describes seven scenarios where they commonly arise. Four of them illustrate the range:

  • You’re expanding a workload into a new jurisdiction and need to identify which obligations apply before you deploy.
  • Regulation restricts who can provide operational support for your workloads, from where, and under what authority.
  • Residency constraints limit your disaster recovery options, and you need recovery paths that hold within approved jurisdictional boundaries.
  • You’re adopting emerging technology such as generative AI, and need to confirm that new data flows and dependencies don’t undermine existing sovereignty controls.

If one or more scenarios match your workload, the lens applies to you.

How to use the lens

The lens works with the AWS Well-Architected Tool. Import it as a custom lens, select a workload, and run a review. The review identifies high- and medium-risk issues, which you prioritize and address through targeted improvement plans. This grounds sovereignty decisions in evidence rather than assumptions.

For your first review, include participants from engineering, legal, compliance, and security. Together, they can connect applicable obligations to workload evidence, prioritize risks, and agree on remediation plans. Record assumptions, accepted risks, owners, and follow-up actions. Repeat the review when regulations, workloads, dependencies, or operating conditions change.

Getting started

The Digital Sovereignty Lens is available today in the AWS Well-Architected custom lens GitHub repository. Download the lens definition, import it into the AWS Well-Architected Tool, and run your first review.

To learn how AWS builds sovereign-by-design infrastructure and controls, visit AWS Digital Sovereignty. For help addressing technical and operational sovereignty requirements, consider engaging AWS Digital Sovereignty Competency Partners.

In 2022, we pledged control without compromise. The Digital Sovereignty Lens is how you architect for it.


About the authors

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Announcing the AWS Digital Sovereignty Lens for the Well-Architected Framework”,
“datePublished”: “2026-10-05 17:54:00”,
“image”: “https://d2908q01vomqb2.cloudfront.net/fc074d501302eb2b93e2554793fcaf50b3bf7291/2026/10/02/REVBLOG-1296-featured-image-1.png”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://aws.amazon.com/blogs/architecture/announcing-the-aws-digital-sovereignty-well-architected-lens/”,
“mainEntityOfPage”: “https://aws.amazon.com/blogs/architecture/announcing-the-aws-digital-sovereignty-well-architected-lens/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

Long onboarding times can cause cybersecurity skill decay

0

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.hrdive.com

Dive Brief:

  • Despite the fast-paced, high-pressure nature of cybersecurity, onboarding represents an efficiency drag, with 57% of leaders in the sector reporting that it takes new hires six months to reach full productivity, according to research published Sept. 29 from cybersecurity training firm SkillBit.
  • Nonetheless, two-thirds of companies want their new cybersecurity hires to get fully up to speed in three months, per the report. In addition, 39% of cybersecurity leaders also said skills decay was a significant concern, with that percentage increasing to 60% among companies with more than 50,000 employees.
  • The report found that even in a high-demand, high-skill workforce like cybersecurity, there were recruiting, hiring and onboarding issues that could slow the talent pipeline.

Dive Insight:

The 2026 Micro-Training Survey Report, created in partnership with CyberBay and Bellini Capital, culled responses from more than 200 cybersecurity leaders.

When it comes to hiring, narrow expertise was less important than versatility, with more than two-thirds of survey respondents citing problem-solving, critical thinking and adaptability over “expertise tied to a specific technology stack.” Even so, 70% of companies said they had “few or no roles available” for applicants with less than two years’ experience.

“Organizations face challenges across the talent lifecycle, from onboarding new hires to keeping experienced professionals current as technologies and attack methods evolve,” the report said. These issues can be exacerbated by the stress to fill empty positions on cybersecurity teams who are “under pressure to defend against increasingly sophisticated threats.”

The report underscored a troubling cycle, whereby companies took “too long to build readiness” and subsequently risked facing a skills decay. 

To prevent losing critical skill sets, the research suggested companies work toward a state of continuous readiness by combining ongoing assessment with hands-on practice and shorter learning cycles.

Leaders in the sector said they overwhelmingly favor more concise, ongoing development processes, with 71% saying they preferred weekly 20-minute learning experiences instead of 30 to 40 hours of training that was offered only once or twice a year.

The results suggest that there are limits to the results that can be achieved through traditional development models such as periodic courses, point-in-time certifications and completion-based measures. Instead, the research found that as artificial intelligence capabilities become more advanced, cybersecurity attack methods and security protocols will also improve, which means companies need to develop more responsive training systems to validate cybersecurity team skills.

“A completed course or certification documents a moment in time,” SkillBit CEO Roman Bohuk said in a statement. “Security leaders need to know whether teams can perform today and be ready for tomorrow’s challenges. Continuous Readiness gives organizations a practical way to build, validate, and strengthen skills before those skills are tested in a real incident.”

Building more nimble workforce training methods can also benefit sectors outside of technology. A recent report from cloud learning platform TalentLMS found that of 1,500 U.S. managers and employees surveyed, nearly half (47%) said some of their job skills became outdated in the last five years, with 21% of managers saying their skills became outdated the last year. In addition, 38% of managers said that AI often made it difficult to know what skills their team would need in the year ahead.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Long onboarding times can cause cybersecurity skill decay”,
“datePublished”: “2026-10-06 15:22:00”,
“image”: “https://imgproxy.divecdn.com/RW84LTt_yEm9Z8nBLnxdZyhIak4khyklnJmuJ-Rb3Vw/g:nowe:0:470/c:3200:1807/rs:fit:770:435/Z3M6Ly9kaXZlc2l0ZS1zdG9yYWdlL2RpdmVpbWFnZS9QWExfMjAyNjA4MDdfMTYxNTQ4NzA2Lk1QLmpwZw==.webp”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.hrdive.com/news/long-onboarding-times-can-cause-cybersecurity-skill-decay/832224/”,
“mainEntityOfPage”: “https://www.hrdive.com/news/long-onboarding-times-can-cause-cybersecurity-skill-decay/832224/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

9 Major Netflix Originals That Could Leave in 2027

0
Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.whats-on-netflix.com

Picture Credit: Netflix

As we look ahead to 2027, the Netflix library is preparing for a massive shift. While we usually expect licensed third-party movies and shows to come and go, the concept of a “Netflix Original” leaving the platform still catches many subscribers off guard. Whether it’s due to expiring 10-year exclusive distribution deals, indie acquisitions, or co-production rights reverting to original networks, several heavy hitters are on the chopping block next year.

Before we dive into the complete master list in a few weeks, let’s tee things off with 10 of the biggest Netflix Originals expected to depart in 2027, but a quick major warning:

Please note: All removals from Netflix are subject to change due to licensing agreements. Netflix may extend licenses or remove titles earlier than listed. Removal dates may also vary by region.


1. The Get Down

Expected to Leave Netflix: April 7, 2027
Who owns the rights? Sony Pictures Television

The Get Down Uauy3JThe Get Down Uauy3J

Picture Credit: Netflix

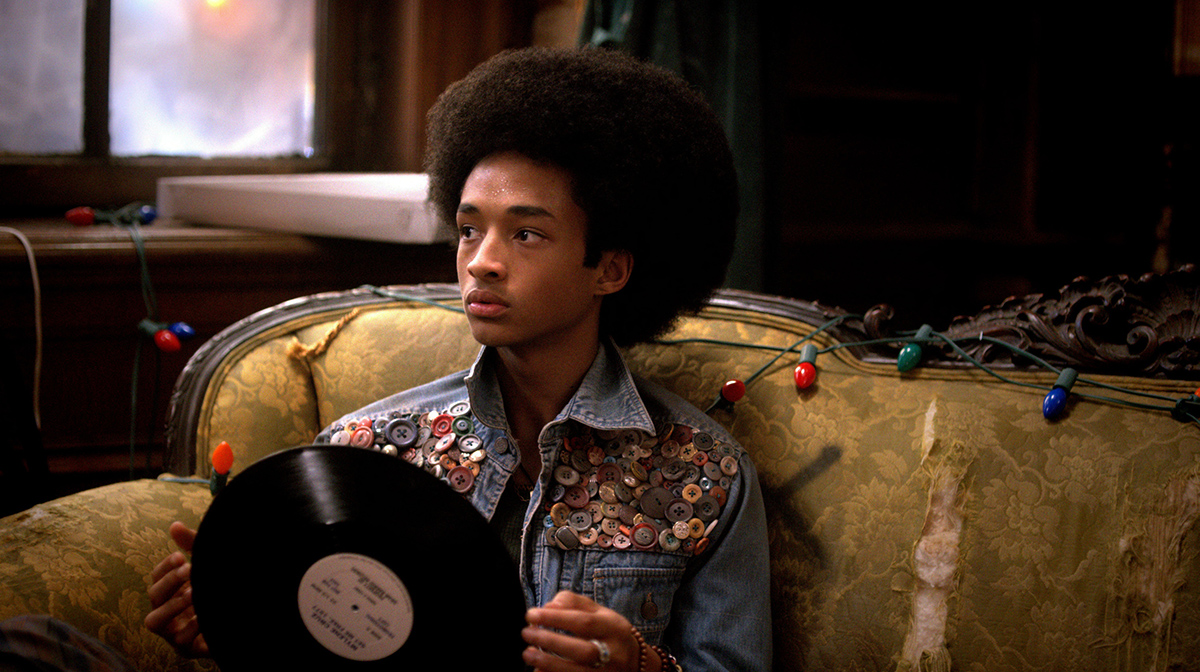
Baz Luhrmann’s incredibly ambitious, big-budget musical drama was a visual and auditory feast. Set in 1977 New York City, the series chronicled the talented and soulful youth of the South Bronx chasing dreams and breakneck beats to transform music history. Despite only lasting one season, it remains a cult favorite in Netflix’s back catalog, albeit it never quite got the viewership needed to justify the price tag on a second season. Part of Netflix’s early prestige lineup, the rights come up next year, aligning with Part 2 of the series dropped on April 7, 2017; its departure date marks exactly 10 years since the final episodes arrived.


2. Bloodline

Expected to Leave Netflix: May 26, 2027
Who owns the rights? Sony Pictures Television

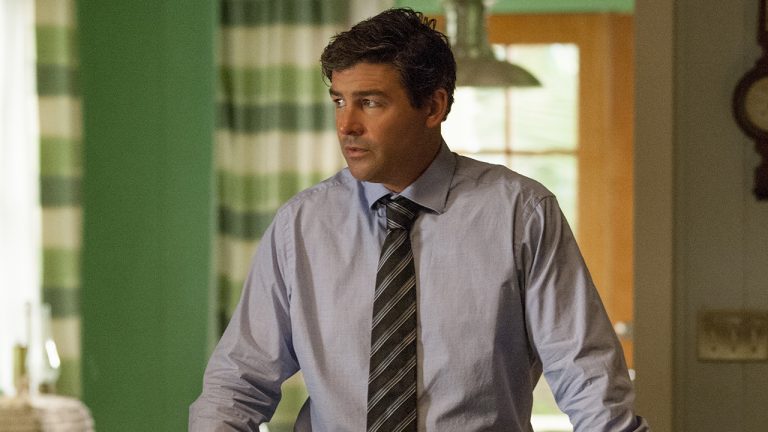
An early prestige darling for the streamer, Bloodline boasted an incredible cast including Kyle Chandler, Ben Mendelsohn, and Sissy Spacek. The slow-burn thriller about a respected Florida family whose dark secrets are threatened by the return of their black sheep son helped cement Netflix as a destination for Emmy-caliber television. Just like The Get Down, Sony leased the show to Netflix. With the third and final season premiering on May 26, 2017, the 10-year clock is finally running out.


3. Glitch

Expected to Leave Netflix: June 1, 2027
Who owns the rights? NBCUniversal / Australian Broadcasting Corporation (ABC)

Glitch Zru9TvGlitch Zru9Tv

Picture Credit: Netflix

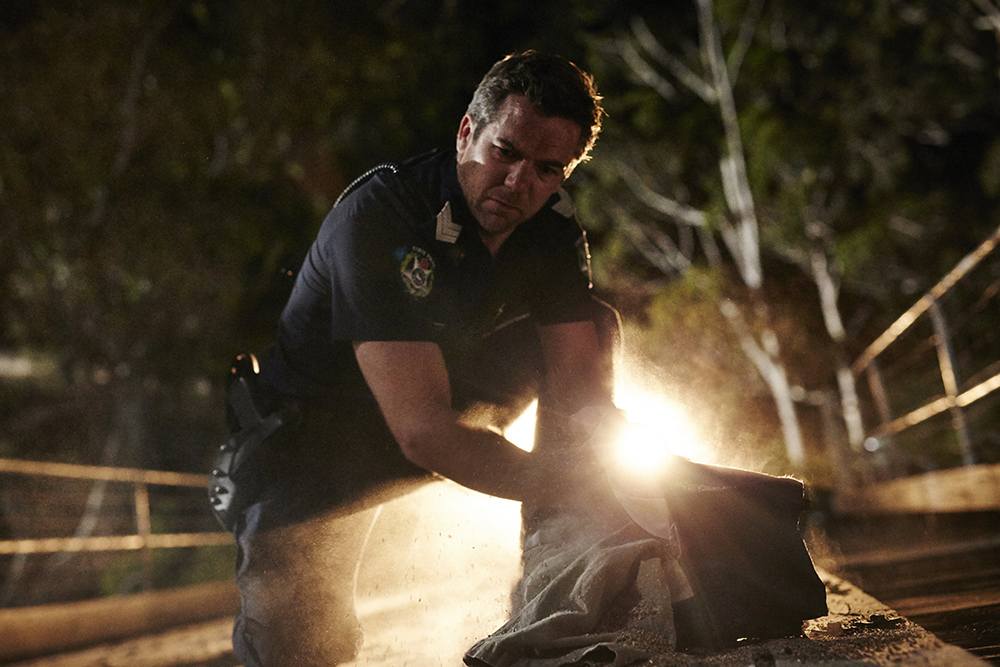
This gripping paranormal drama became a massive sleeper hit for Netflix globally. The series kicks off with a chilling premise: a police officer and a doctor are faced with an emotionally charged mystery when six local residents inexplicably claw their way out of their graves in peak physical form. Glitch is a classic international co-production. It originally aired on the ABC network in Australia and was produced by Matchbox Pictures (a subsidiary of NBCUniversal). Netflix boarded the project to act as the global distributor, but the underlying rights belong down under.


4. Shimmer Lake

Expected to Leave Netflix: June 9, 2027
Who owns the rights? Footprint Features / Writ Large

This inventive, darkly comic crime thriller stands out for its unique narrative structure, unfolding entirely in reverse time. Starring Rainn Wilson, Benjamin Walker, and Rob Corddry, the film follows a local sheriff relentlessly hunting three bank robbery suspects. Financed independently by Footprint Features and Writ Large, Netflix purchased the exclusive global streaming rights to release it as an Original. Released on June 9, 2017, its removal exactly a decade later is another textbook contract expiration.


5. To the Bone

Expected to Leave Netflix: July 14, 2027
Who owns the rights? AMBI Group

Starring Lily Collins and Keanu Reeves, this indie drama sparked widespread discussion upon its release. The film follows Ellen, a 20-year-old with anorexia nervosa, who goes on a harrowing journey of self-discovery at a group home. Following a massive bidding war at the 2017 Sundance Film Festival, Netflix purchased the worldwide rights for $8 million from the film’s indie financiers (AMBI Group and Mockingbird Pictures). Ten years later, those rights are reverting.


6. Tales of Arcadia

Expected to Leave Netflix: July 21, 2027
Who owns the rights? DreamWorks Animation / NBCUniversal

Tales Of ArcadiaTales Of Arcadia

Picture Credit: Netflix

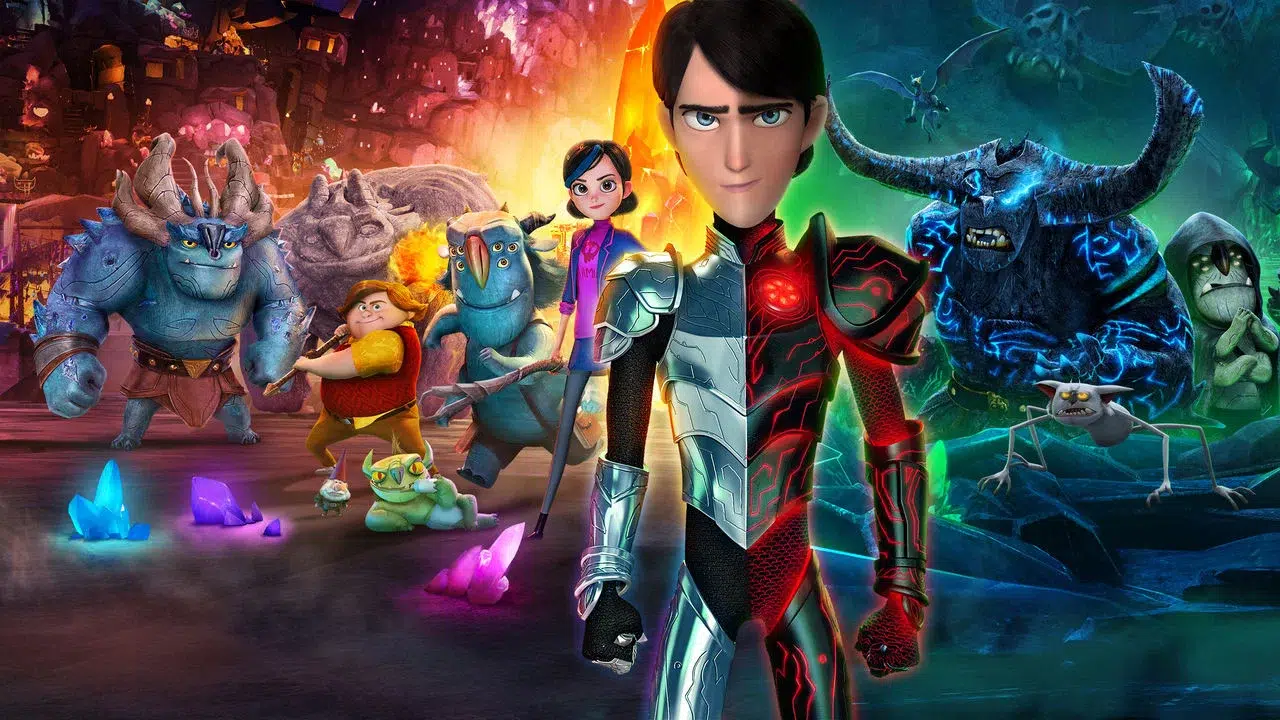
Created by visionary director Guillermo del Toro, this wildly popular animated series kicked off the entire Tales of Arcadia universe. Following an average teen who uncovers a mysterious amulet to save two worlds, it is one of the streamer’s most acclaimed family shows. However, Trollhunters was born out of a massive output deal Netflix struck with DreamWorks Animation. DreamWorks (now completely owned by NBCUniversal) owns the IP and characters, and like much of their other output, we’ve seen the titles depart over the years, but sadly many have never really found new permanent homes. 


7. The Incredible Jessica James

Expected to Leave Netflix: July 28, 2027
Who owns the rights? Beachside Films

Another gem acquired by Netflix after making waves at Sundance, this delightful indie rom-com is driven by incredible chemistry between its leads. A struggling New York City playwright (Jessica Williams) makes an unlikely connection with a divorced app designer (Chris O’Dowd) she meets on a blind date. Produced by the indie company Beachside Films, Netflix bought the worldwide streaming rights for over $3 million. It debuted on July 28, 2017, meaning it will depart exactly 10 years to the day.


8. Alias Grace

Expected to Leave Netflix: November 3, 2027
Who owns the rights? Halfire Entertainment / CBC

Alias Grace Xnyo71Alias Grace Xnyo71

Picture Credit: Netflix

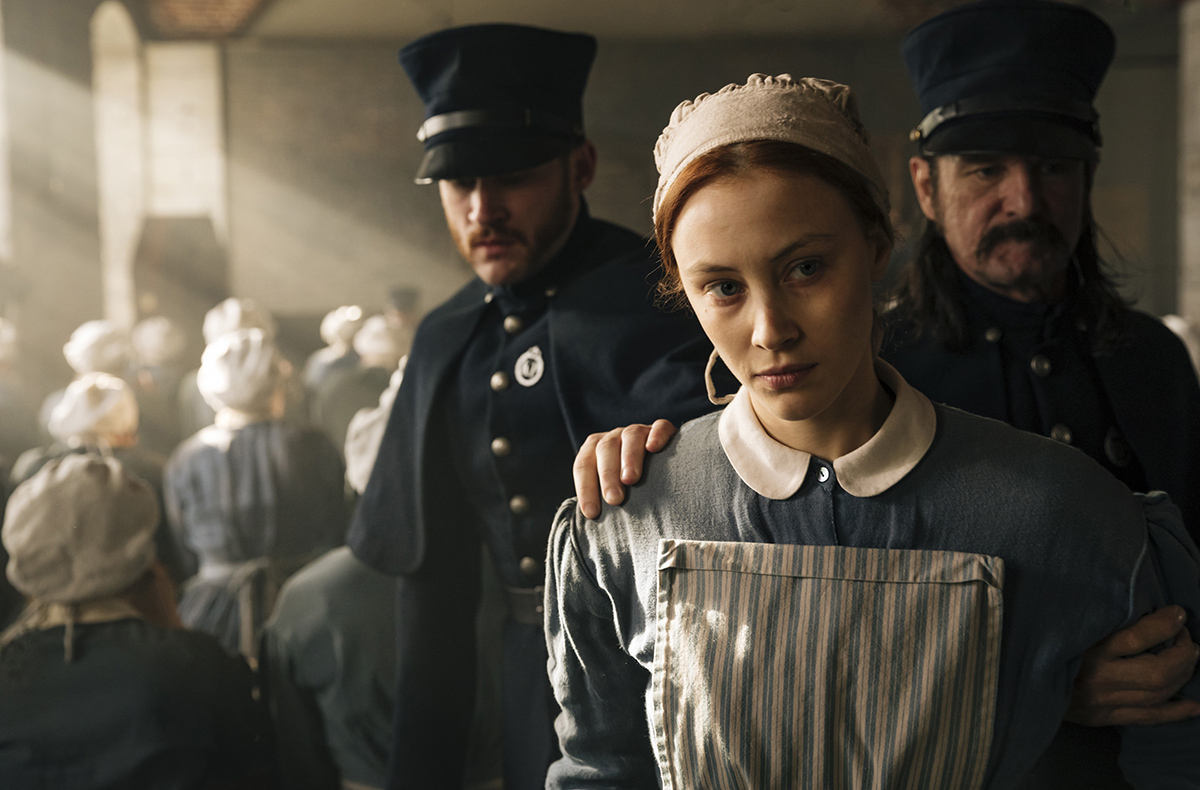
Based on the award-winning novel by Margaret Atwood (The Handmaid’s Tale), this gripping 19th-century Canadian true-crime miniseries asks whether a convicted murderess should be pardoned due to insanity. Earning widespread critical acclaim, this was a co-commission between the Canadian Broadcasting Corporation (CBC) and Netflix. Netflix secured the rights to brand it as an Original outside of Canada starting on November 3, 2017. Unless a new deal is struck, this prestige drama will be gone by the holidays.


9. Fast & Furious Spy Racers

Expected to Leave Netflix: November 7, 2027
Who owns the rights? Universal Pictures / DreamWorks Animation

Expanding the blockbuster Fast & Furious cinematic universe, this animated hit recruited teen driver Tony Toretto and his thrill-seeking friends to infiltrate a criminal street racing circuit. The Fast & Furious brand is one of Universal Pictures’ most lucrative crown jewels. Through their DreamWorks television wing, they produced this show and licensed it to Netflix. Because Universal owns the IP, Netflix was only ever “renting” the Toretto crew.


Once again: Removals are always subject to change! Deals are incredibly fluid, and Netflix occasionally swoops in to re-license or renew titles (like they recently did with Call My Agent! and Rita) before they officially depart.

Which of these Netflix Originals will you be saddest to see leave in 2027? Let us know in the comments below!

Going to Concerts Alone Is a Top-Tier Human Experience

0
Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.rollingstone.com

Over the weekend, DeuxMoi, the notorious Instagram gossip account known for its celebrity sightings and blind items, shared an Instagram Story post featuring a screenshot of a message from a reader who reported seeing comedian Martin Herlihy getting a drink alone at Phoebe Bridgers’ concert at Barclays Center. Bridgers’ tour restricts phones, so the reader’s account had to stand in for the clandestine photo that might otherwise have accompanied the sighting.

“Phoebe’s great, but going to a phoebe show solo seems a little sad,” the reader wrote. Another attendee had asked Herlihy for a hug, which he gave, but the reader dismissed the encounter as “a moot point since no photos!”

The internet has summarily ridiculed the (thankfully) anonymous user, who, in psychoanalyzing the decision to attend a concert alone, both confirmed the reason for no phone policies at shows and illustrated how ingrained the surveillance-driven ethos of these invasive little devices in our pockets has become. 

“Cannot imagine anything more lame than opening the Instagram app and messaging Deuxmoi,” one X user posted. 

The reader also makes an unforced judgment error. Going to concerts alone is decidedly not sad. Beyond the fact that Phoebe Bridgers is probably the ideal concert to attend by oneself, going out to see a show alone is one of life’s great pleasures. 

Of course, it’s a grand experience to meet up with a bunch of friends at the show, or dance in the embrace of a significant other, but being at a show alone offers a more personal kind of intimacy that, increasingly, is hard to find. 

For one, at least in an ideal world, you’re able to blend into the mass of the crowd, whose attention — again, in an ideal world — is laser focused on the stage, a shared object of adoration that finds you in communion with complete strangers, enraptured in something near-religious and sometimes even explicitly so, the human spirit dialed to a frequency that alone or in a group you get to tap into for a brief moment, experiencing the oneness of all things — unless you’re staring at your phone or looking around for celebrities to call out.  

Trending Stories

The post about Herlihy calls to mind the return to concerts of the early post-COVID era. When concertgoers became notorious for all manner of anti-social behavior, from throwing random stuff on stage to shouting disruptive comments during sets, that many concluded was a result of spending so much time in isolation. Even as the world has gotten more accustomed to live events, the more pernicious tendency these days is the constant surveillance from people on their phones, hoping the real world experience unfolding in front of them might have some cultural value on the clout web. 

It’s the kind of thinking that forges a self-conscious stance that can’t imagine enjoying a concert alone. How can you enjoy anything, to say nothing of quality time with yourself, if you can’t for a second imagine your life unfolding anywhere but on a feed.

YouTuber, 3 others held for assault inside police station | Dehradun News

0
Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: timesofindia.indiatimes.com
YouTuber, 3 others held for assault inside police station Dehradun: YouTuber and social media influencer Anurag Dobhal, who runs a channel with purportedly more than 8 million followers, was arrested along with three others for allegedly assaulting his brother-in-law on a busy road and later inside a police station here on Monday night.The other arrested accused were Abhishek Kumar (22) from Saharanpur; Abhay Choudhary (23) from Haridwar; and Qurban (23) from Panipat.Police said the four, along with three others — Tapan Pandit, Dhaval Rajpurohit and Abhinav Srivastava — were named in an FIR filed on the complaint of Dobhal’s brother-in-law, Raj Singh Chauhan, a Dehradun resident.Dehradun SSP Pramendra Dobal said police control room personnel received a call reporting a brawl on a busy road in Nehru Colony area. A team reached the spot and found the four men allegedly assaulting Chauhan.“All of them were taken to the police station to resolve the matter. However, the four again assaulted him inside the station,” Dobal said.The accused were initially detained under section 170 of the BNSS. An FIR was subsequently registered under BNS sections 117(2) (voluntarily causing hurt), 191(2) (rioting) and 351(3) (aggravated criminal intimidation). Police said efforts were underway to trace the three absconding accused.

Polisario rejects ‘half-solutions’ as UN Security Council prepares to review Western Sahara mission

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.tamilguardian.com

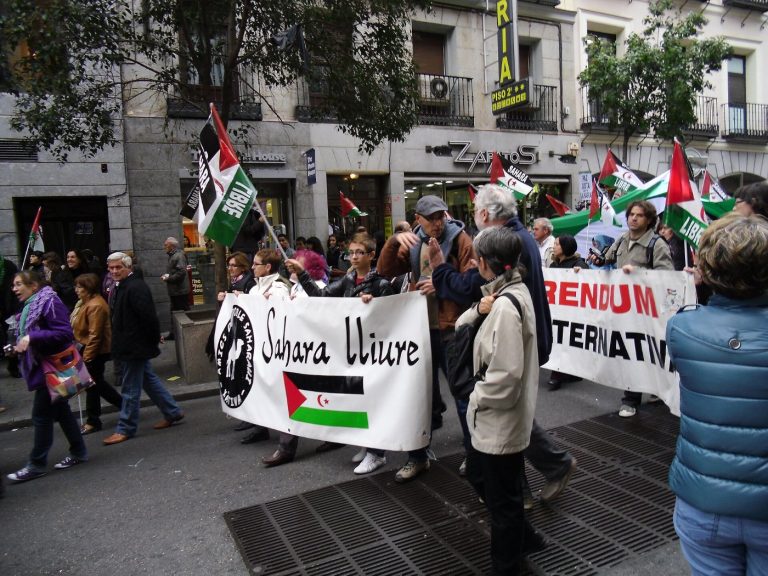
File photograph: A demonstration in Madrid in support of the Sahrawi people, November 2010. Photo: Cristianrodenas / Wikimedia Commons, CC BY-SA 3.0

The Polisario Front has said it will reject any “half-solutions” that circumvent the Sahrawi people’s right to self-determination and independence, as the UN Security Council prepares to discuss Western Sahara and renew the mandate of its mission in the territory this month.

Sidi Mohamed Omar, the Polisario Front’s representative to the UN and its coordinator with the UN Mission for the Referendum in Western Sahara (MINURSO), said the movement would refuse “to enter into any discussion intended to prejudice our people’s right to self-determination”, the Sahara Press Service reported.

Speaking to Sahrawi TV on Sunday, he said the Polisario would only discuss measures that enable the Sahrawi people “to freely determine their own destiny”, and that they were prepared to make sacrifices to defend their rights.

He said the Security Council would hold its first session on Thursday to hear briefings from the UN Secretary-General’s personal envoy for Western Sahara, Staffan de Mistura, and the head of MINURSO, Alexander Ivanko.

Autonomy ‘as a basis’

The Council is expected to vote this month on renewing MINURSO’s mandate, which expires on 31 October, according to Security Council Report.

Last year’s resolution 2797 backed negotiations taking Morocco’s autonomy proposal as a basis. The plan, submitted in 2007, would integrate the territory into Morocco. The resolution also referred to a solution that “provides for the self-determination of the people of Western Sahara”.

The United States, which drafts the Council’s resolutions on Western Sahara, recognised Moroccan sovereignty over the territory in 2020. France backs the autonomy plan as the “only basis” for a solution, while the UK calls it the “most credible, viable and pragmatic basis”. Pakistan, which has emphasised self-determination, abstained on last year’s resolution.

Talks hosted by the US in Madrid and Washington in February brought together Morocco, the Polisario Front, Algeria and Mauritania for the first time since 2019, but made no progress in narrowing their differences.

Continuing hostilities

MINURSO was established in 1991 to organise a referendum on self-determination for the Sahrawi people, which has never been held. The Polisario Front ended its ceasefire with Morocco in 2020.

Hostilities have continued at a low to medium intensity. In May, rockets struck near Smara in Moroccan-administered Western Sahara, an attack claimed by the Polisario, and in June a reported Moroccan drone strike east of the berm killed the senior Polisario figure Lahbib Mohamed Abdelaziz and two others.