Home Blog Page 12

Every James Bond Film Is Now Streaming On Amazon Prime Video

0
Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.huffingtonpost.co.uk

As the world continues to wait on any crumb of information on the future of the James Bond franchise, fans now have a fresh opportunity to catch up on the existing films in the series.

Earlier this week, all 25 instalments in the regular James Bond canon were made available to stream on Amazon Prime Video, beginning with 1962’s Dr. No right through to the most recent addition, 2022’s No Time To Die.

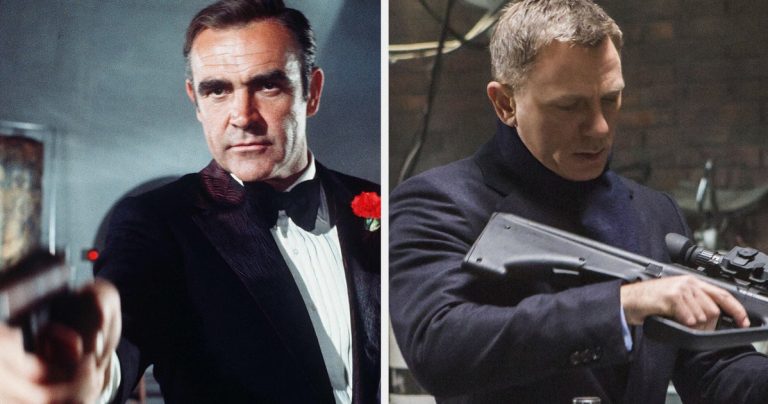
Daniel Craig is the most recent actor to play James Bond on the big screen

Columbia/Eon/Danjaq/Mgm/Kobal/Shutterstock

It’s no great surprise that Prime Video would become the films’ primary streaming home, after Amazon acquired the films’ production company MGM in 2022, and took over creative control of the movies last year.

However, it’s not just the main James Bond films that 007 fans can enjoy on Prime Video…

Which James Bond films are now streaming on Amazon Prime Video?

All 25 films in the established James Bond canon are now available to stream.

  • Dr No
  • From Russia With Love
  • Goldfinger
  • Thunderball
  • You Only Live Twice
  • On Her Majesty’s Secret Service
  • Diamonds Are Forever
  • Live And Let Die
  • The Man With The Golden Gun
  • The Spy Who Loved Me
  • Moonraker
  • For Your Eyes Only
  • Octopussy
  • A View To Kill
  • The Living Daylights
  • Licence To Kill
  • GoldenEye
  • Tomorrow Never Dies
  • The World Is Not Enough
  • Die Another Day
  • Casino Royale
  • Quantum Of Solace
  • Skyfall
  • Spectre
  • No Time To Die

In addition, two more James Bond films not in collaboration with Eon are also streaming on Prime Video – the 1960s spoof Casino Royale and the unofficial Sean Connery outing Never Say Never Again.

There’s also the two-season reality competition series 007: Road To A Million, in which pairs of contestants are put through their paces in a series of Bond-esque challenges – overseen by a new Bond villain, played by Brian Cox – to try and bag a £1,000,000 cash prize.

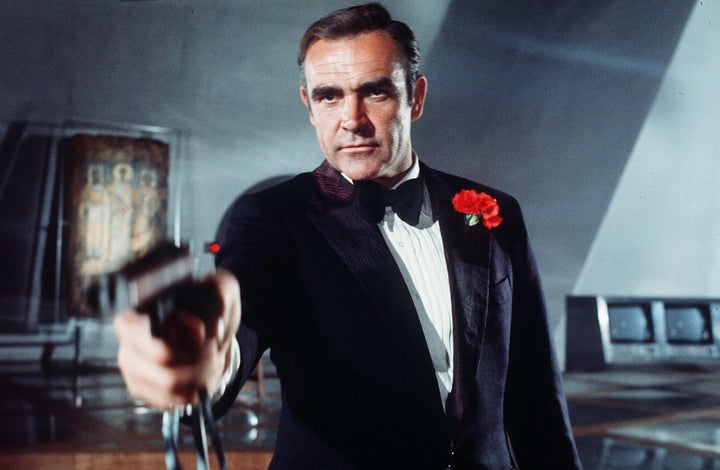
Sean Connery as James bond in Diamonds Are Forever

Danjaq/Eon/Ua/Kobal/Shutterstock

What do we know about the next James Bond film?

Well, at the time of writing, frustratingly little.

Dune filmmaker Denis Villeneuve is set to direct the 26th instalment in the James Bond series, with Peaky Blinders and House Of Guinness creator Steven Knight writing the script.

It’s still not clear who will be starring in the film, although recent reports have indicated that Heartstopper’s Jack Barton and Slow Horses’ Jack Lowden are the top choices for the job.

Other names rumoured to still be in consideration include Jacob Elordi, Callum Turner, Harris Dickinson and Paul Mescal.

The Only 2 Artificial Intelligence (AI) Stocks I’d Buy With $1,000 Today and Never Sell

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.fool.com

When I invest in artificial intelligence stocks, I look for low-market-cap companies with high revenue growth. That basic formula points me toward growth stocks that haven’t yet become household names. That strategy explains why these two AI stock picks are among the largest positions in my portfolio. If you have $1,000 (or more) that you’re ready to put to work in the stock market today, they’re worth a look.

Image source: Getty Images.

1. Iren

Iren (IREN -3.06%) builds AI data centers that provide critical compute for hyperscalers. It has already signed long-term deals with Microsoft (MSFT +1.48%), Nvidia (NVDA +2.12%), and various AI enterprises. That customer validation and Iren’s knack for building AI data centers on time position it as one of the top neoclouds.

Iren Stock Quote

Today’s Change

(-3.06%) $-1.28

Current Price

$40.48

A look at the key numbers indicates how big its opportunity could become. Iren reported $137.2 million in revenue for its fiscal 2026 fourth quarter, which ended June 30. That was down 27% year over year, and that fact in isolation might make Iren seem like a bad business to invest in. However, it’s on track to reach $4 billion in annual recurring revenue by the end of the calendar year. That means the revenue growth rate will go up substantially in future quarters.

Iren’s revenue comes from providing AI compute capacity to tech leaders. It’s getting annual contract values above $20 million per megawatt, with short-term deals currently being negotiated at $25 million per megawatt. Iren has a 5,800-megawatt pipeline, so once all of the projects it’s developing are brought online, the entire portfolio could generate $145 billion in annual recurring revenue, assuming the $25-million-per-megawatt rate holds.

Megawatt prices have more than doubled in less than a year, so the types of contracts Iren can command may be much higher by the time it brings capacity online. Iren is on track to deliver an additional 800 megawatts in 2027, with large customer prepayments covering a large percentage of capital expenditures.

2. Netlist

Netlist (NLST -0.18%) trades as an over-the-counter (OTC) security rather than being listed on a national exchange. Back in 2018, when its share price sank consistently below $1, management chose to allow the company to be delisted from the Nasdaq rather than performing a reverse stock split. Today, after a year-to-date gain of more than 500%, it trades at around $5.50.

Netlist Stock Quote

Today’s Change

(-0.18%) $-0.01

Current Price

$5.65

Buying OTC stocks can be a bit riskier, as they are not subject to the same regulatory standards as those traded on the major exchanges, and may not reveal as much of their business and financial data. Moreover, not all OTC stocks have solid business models. However, Netlist more than doubled its revenue year over year, driven by memory product sales and royalties. If it relists with Nasdaq in the future, a meaningful rerating may occur.

While Netlist’s CXL products could eventually be a major part of revenue growth, litigation is the main catalyst driving its growth right now. Netlist has accused memory chip giants of infringing multiple patents for key products.

Its success in these patent lawsuits so far has already translated into meaningful revenue, including a landmark five-year deal with Samsung (SSNLF +0.00%) that will pay Netlist approximately $27.5 million per quarter. That deal also came with a $200 million up-front license fee and the ability to buy $300 million in memory products from Samsung annually for the next five years, giving Netlist some insulation from supply shortages.

Netlist has SK Hynix (SKHY -0.06%) in a similar arrangement and should renew the deal this year. Most of those royalties are pure profit. Micron (MU -1.02%) has been a holdout in these negotiations, but a $445 million verdict in Netlist’s favor, the looming threat of cease-and-desist orders, and a recently announced U.S. International Trade Commission investigation into Micron and others concerning Netlist patents suggest a lucrative resolution is on the way.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: ” The Only 2 Artificial Intelligence (AI) Stocks I’d Buy With $1,000 Today and Never Sell”,
“datePublished”: “2026-10-06 12:38:00”,
“image”: “https://g.foolcdn.com/image/?url=https%3A%2F%2Fg.foolcdn.com%2Feditorial%2Fimages%2F890042%2Fgettyimages-2230233284-1201×800-5b2df79.jpg&w=1200&op=resize”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.fool.com/investing/2026/10/06/the-only-2-artificial-intelligence-ai-stocks-id-bu/”,
“mainEntityOfPage”: “https://www.fool.com/investing/2026/10/06/the-only-2-artificial-intelligence-ai-stocks-id-bu/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

Google overhauls cloud modernization portfolio with new AI agents

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.networkworld.com

The new Hub, which will be accessible via the Google Cloud Console, will also be a part of the umbrella offering, the company wrote.

For CIOs, the consolidation of existing modernization and migration tools under a broader umbrella offering could simplify operations and decision-making as it turns what was previously a collection of separate tools into “one end-to-end process”, said Pareekh Jain, principal analyst at Pareekh Consulting.

“An enterprise might have VMware workloads, Java applications, mainframes, Oracle databases and Kubernetes applications running across different clouds. Previously, these could require separate tools, assessments and migration teams. With the broader offering, CIOs require fewer handoffs, faster decisions and better visibility across a large modernization program,” Jain said.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: ” Google overhauls cloud modernization portfolio with new AI agents”,
“datePublished”: “2026-10-06 12:11:00”,
“image”: “https://www.networkworld.com/wp-content/uploads/2026/10/4231147-0-87120200-1791288565-shutterstock_1914949381-Cropped-1.jpg?quality=50&strip=all&w=1024”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.networkworld.com/article/4231147/google-overhauls-cloud-modernization-portfolio-with-new-ai-agents.html”,
“mainEntityOfPage”: “https://www.networkworld.com/article/4231147/google-overhauls-cloud-modernization-portfolio-with-new-ai-agents.html”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

Book Review: ‘The AGI Chronicles,’ by Kevin Roose

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.nytimes.com

As Roose writes, artificial intelligence circa 2016 was good at getting computers to excel at single, directed goals. The big leap forward came when Radford and his colleagues discovered that L.L.M.s, engorged with enough training data, could learn how to do things no one had asked or programmed them to do. What started as the simple task of predicting the next chunk of language in a partly written sentence would become, a decade later, a form of unpredictable technology capable of spawning rogue A.I. agents adept at deceiving their human masters and apparently willing to exert peer pressure on one another to spread into places they were specifically asked not to go.

It’s striking that so many A.I. executives have spoken, openly and at length, about their technology’s possibly destructive power, which is an odd position for people trying to sell a product to find themselves in. Roose is careful, and correct, to separate the two questions every lay person has about A.I.: How much damage could it really cause? and Is it in any sense truly thinking? The discourse around A.I. blurs these two questions constantly. Roose, a journalist rather than a cultural judge, does not.

He wisely leaves the forecasting to his protagonists, though he does a good job of evoking their specific temperaments. Amodei: prickly, monkish, intermittently principled; OpenAI’s Sam Altman: grinning, slippery, strapped with an array of metaphorical office shivs; and Hassabis: brilliant, stubborn, covetous of recognition. In following their work, Roose lets them be as messy and confounding as they’ve publicly shown themselves to be, even for those who’ve only loosely followed their striving, infighting and messiness.

That messiness is where the book is most fun. Roose writes, for instance, that when the Biden White House convened an A.I. symposium in 2023, Mark Zuckerberg’s Meta was not invited. This was quite distressing to Zuckerberg, who had skillfully pivoted from wasting billions on his Metaverse to wasting billions on machine learning. A Meta rep called the White House to complain, eliciting this response: “I’m sorry. Do you guys do A.I.?”

Or take Ilya Sutskever, OpenAI’s onetime chief scientist, whose office mantra (“Feel the A.G.I.”) outlived his own brief, failed corporate putsch against Altman in November 2023. Then there’s the Google co-founder Sergey Brin, whose competitive fire was reignited by the race to A.G.I., and who had badged back into Mountain View that spring after a few years of retirement only to find himself working directly alongside engineers young enough to idolize him and old enough to resent his proclamation that they weren’t working enough hours.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: ” Book Review: ‘The AGI Chronicles,’ by Kevin Roose”,
“datePublished”: “2026-10-06 09:00:00”,
“image”: “https://static01.nyt.com/images/2026/10/11/books/11TBR-Roose-MAIN/11TBR-Roose-MAIN-facebookJumbo.jpg”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.nytimes.com/2026/10/06/books/review/the-agi-chronicles-kevin-roose.html”,
“mainEntityOfPage”: “https://www.nytimes.com/2026/10/06/books/review/the-agi-chronicles-kevin-roose.html”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}

FBI Drops Accenture Contractor After Sensitive Data Breach
0

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: securityaffairs.com

FBI Drops Accenture Contractor After Sensitive Data Breach

Pierluigi Paganini
October 06, 2026

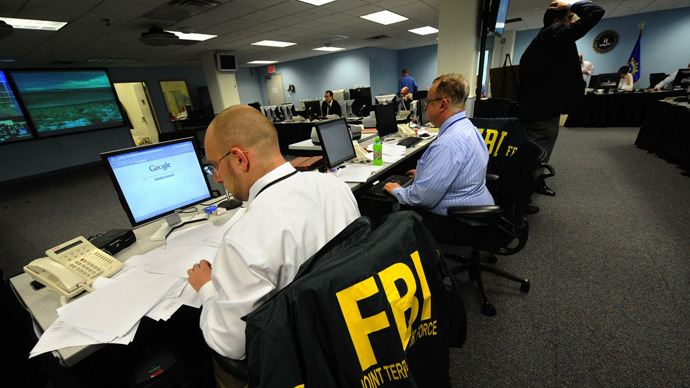
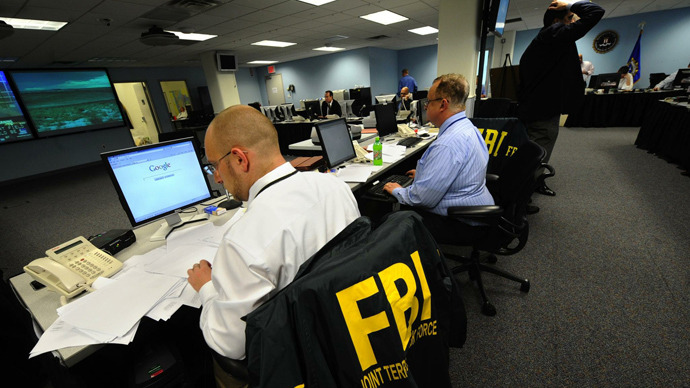
Accenture lost an FBI contract after a missed security patch exposed sensitive employee data, raising serious concerns over operational security.

The FBI pulled an Accenture contractor off its account on Monday, and the reason is almost mundane compared to the damage it caused. One update didn’t get installed on time.

“The ‌Federal Bureau of Investigation removed an Accenture contractor on Monday over their role in a damaging data breach that exposed sensitive personal details of thousands of bureau employees, two sources familiar with the matter told Reuters.” Reuters reports. “The development comes as the FBI is still trying to ascertain the ramifications of the breach, ​which some former bureau officials have described as a major blow to the organization’s operational security.”

Two sources told Reuters the bureau cut ties with the contractor over their role in a breach that exposed sensitive personal data on thousands of FBI employees. Former bureau officials are calling it a serious hit to the organization’s operational security, not just an embarrassing headline. That’s a strong statement coming from people who used to run the place.

“To date, our review has determined that the incident occurred as the result of a security failure ​of a platform managed by a third-party organization — after a contractor failed to implement a security patch explicitly issued to secure the ​platform,” FBI cyber chief Brett Leatherman said in the statement to Reuters. “As such, the FBI has removed the contractor and taken all necessary steps to both mitigate any further risk and protect our workforce.”

FBI cyber chief Brett Leatherman laid out exactly what went wrong in a statement to Reuters. The incident traces back to a platform managed by a third party, where a contractor “failed to implement a security patch explicitly issued to secure the platform.” Not an unknown flaw, not a zero day, a fix that already existed and just didn’t get installed.

Reuters’ sources identified the platform as Oracle PeopleSoft, the human resources software running the FBI’s job site, and named Accenture as the third party managing it. Oracle hasn’t responded to requests for comment. Accenture, for its part, said only that it’s proud to support the FBI’s mission and plans to keep doing so, dodging every question about the contractor or the missed patch.

In June, Google warned about a ShinyHunters-linked campaign targeting PeopleSoft users. On the same day, Oracle issued a security alert about the vulnerability and released a fix. Both companies told PeopleSoft customers to install all critical patches and security updates as soon as possible.

ShinyHunters later said they used this same PeopleSoft vulnerability to access the FBI’s job site. Patching large enterprise systems can be difficult, but this wasn’t an unknown or obscure flaw. It had already been publicly identified, attackers were exploiting it, and a fix was available.

In September, the popular cybercrime group ShinyHunters claimed that it breached the U.S. Federal Bureau of Investigation (FBI) and stole sensitive information belonging to FBI employees and job applicants. The group says the operation was not financially motivated and was instead carried out in response to an FBI warning published earlier this year.

The claim surfaced on September 22 and quickly drew attention after ShinyHunters said it obtained data on a large number of current and former FBI personnel. The group reportedly offered a sample of around 5,000 records as evidence and claimed that the stolen information could include names, addresses, phone numbers, Social Security numbers, assignments and, in some cases, family details.

Reuters was able to partially match some of the sample information with other records, including data associated with FBI Director Kash Patel.

“Reuters was able to partially verify the authenticity of the information by running the details, including the Social Security numbers, ​against credit bureau records and previously breached data preserved by the dark-web intelligence firm District 4 Labs.” reads the report published by Reuters. “In at least 10 instances — including in the case ‌of FBI ⁠Director Kash Patel — Reuters found details that appeared to match. A person familiar with the matter said that the job descriptions in the data also matched in at least some cases.”

The FBI acknowledged that it is aware of claims involving unauthorized activity affecting FBIjobs.gov and said it is investigating. The agency has not confirmed that its internal systems were compromised or that ShinyHunters obtained the data it claims to possess.

ShinyHunters provided a possible technical explanation for the alleged intrusion. The group claims the exploitation of an Oracle PeopleSoft zero-day, reportedly using it to gain remote code execution through infrastructure connected to the FBI’s recruitment services.

The attackers also reportedly claimed access to several FBI-related services, including human resources systems and a system they referred to as Medlink. They allegedly said that between 2 TB and 3 TB of data had been taken and that the FBI jobs infrastructure had been compromised.

There is also a clear motive behind the operation claimed by ShinyHunters. The group says it targeted the FBI after a May 2026 public advisory describing its tactics and warning victims against paying. ShinyHunters disputes the FBI’s characterization of its activities and is reportedly demanding that the Bureau retract or correct the warning.

This makes the alleged attack unusual. Instead of immediately demanding a conventional ransom, the group appears to be using the stolen data as leverage in a dispute with U.S. law enforcement.

The timing is also significant. ShinyHunters has recently claimed responsibility for several major breaches and has been involved in a public dispute with the Clop cybercrime operation. The group recently claimed to have compromised Clop’s data leak site, highlighting the increasingly aggressive behavior surrounding the group.

The stolen data is much more sensitive than the usual names and email addresses seen in data breaches. It includes details about named employees’ counterintelligence roles, home addresses of human intelligence operatives, and medical and psychiatric records of FBI staff.

For an agency where some employees depend on keeping their identities, jobs and home addresses private, this goes beyond a normal data breach. It creates a serious operational security risk.

Last week a key ShinyHunters suspect got picked up in Jordan and reportedly started cooperating with investigators, which might help the bureau understand just how bad the damage really is. Removing one contractor doesn’t undo an exposure like this, it just closes the door after the fact.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Accenture)