
Home Blog Page 21

Generate unit tests for your modernized code with AWS Transform for .NET

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: aws.amazon.com

When you modernize a .NET Framework application to modern .NET, you end up with a transformed, buildable codebase — but the question that immediately follows is always the same: how do I safely keep changing it from here? Once the code is modernized, your team keeps evolving it — fixing bugs, adding features, upgrading dependencies — and each change needs a way to confirm the modernized code still behaves as expected. Building that safety net has always been the developer’s job, and while AI agents now help produce the tests, getting coverage with the ability to catch regressions remains hard. That is exactly the gap the newest AWS Transform for .NET capability closes.

As of September 2026, AWS Transform for .NET can automatically generate unit tests for the code it modernizes. When you enable it, AWS Transform generates unit tests that target the testable classes in your transformed application — business logic, controllers, and the like—giving you an automated test safety net as part of the same job that performs the modernization. In this post, I’ll walk you through how the unit test agent fits into the transformation flow and how to run it after a .NET transformation in Visual Studio.

Why this matters

A previous post walked through a sizeable .NET transformation using the conversational AI assistant in Visual Studio — assessment, plan review, project-by-project transformation, a local build, and a final set of artifacts. At the end of that walkthrough, the result was a transformed solution that built cleanly. But a clean build only tells you it compiles — the modernized code has little or no test coverage to validate future changes. That is where the unit test agent comes in: the tests it generates capture the behavior of the modernized code and become the safety net that guards every future change, so the next edit someone makes can’t quietly break it.

Tests generated against the modernized code establish a behavioral baseline you can build on: every time your team fixes a bug, adds a feature, or bumps a dependency, the test suite tells you whether the change is safe or something regressed. Developers today rarely write all of that coverage by hand — they lean on AI agents to help. The hard part isn’t producing some tests; it’s producing effective ones: high line and branch coverage, ability to catch regressions, tests that run fast, and — critically — coverage generated without altering the original code under test. The unit test agent addresses this directly: it produces test coverage for the modernized code so you finish the modernization with tests already in place, rather than treating test authoring as a separate project that starts after the modernization ends.

How the unit test agent works

The unit test agent runs alongside the standard transformation rather than bolting on afterward. When enabled, AWS Transform:

  1. Assesses your application for testability in parallel with the standard .NET assessment.
  2. Plans which classes and methods to cover — focusing on the testable units such as business logic and controllers.
  3. Generates the corresponding unit test code so the test project is populated as part of the same job that performs the modernization.

The important design choice here is that unit test generation is opt-in, and you have two moments to opt in:

  • At the start of a job — so testability assessment and test generation happen together with the transformation, unattended.
  • After transformation completes — so you can transform first, review the modernized code, and then ask for tests once you’re satisfied with the port.

If unit test generation is enabled as part of the transformation, the tests are generated automatically, without any additional steps from the developer — testability assessment, coverage planning, and test code generation all happen within the same job that performs the modernization.

That flexibility mirrors the rest of the AWS Transform experience: you stay in control of when the agent does work, and you can let it run unattended or drive it interactively.

Prerequisites

To generate unit tests with AWS Transform for .NET, you’ll need the following:

Figure 1: Sign in to AWS Transform in Visual Studio

Unit test generation is available in all AWS Regions where AWS Transform for .NET is supported.

Walkthrough: adding the unit test agent after a transformation

Let me walk through the flow the way you’d actually experience it in Visual Studio.

Step 1: Start a transformation (with tests in mind)

In this step, before starting the transformation setup sample application using following steps using Visual Studio:

  1. Clone git hub sample (https://github.com/aws-samples/bobs-used-bookstore-sample.git) by going to Git → Clone Repository, paste https://github.com/aws-samples/bobs-used-bookstore-sample.git, and choose a local path (Figure 2). Choose Clone which is .NET 10 sample.
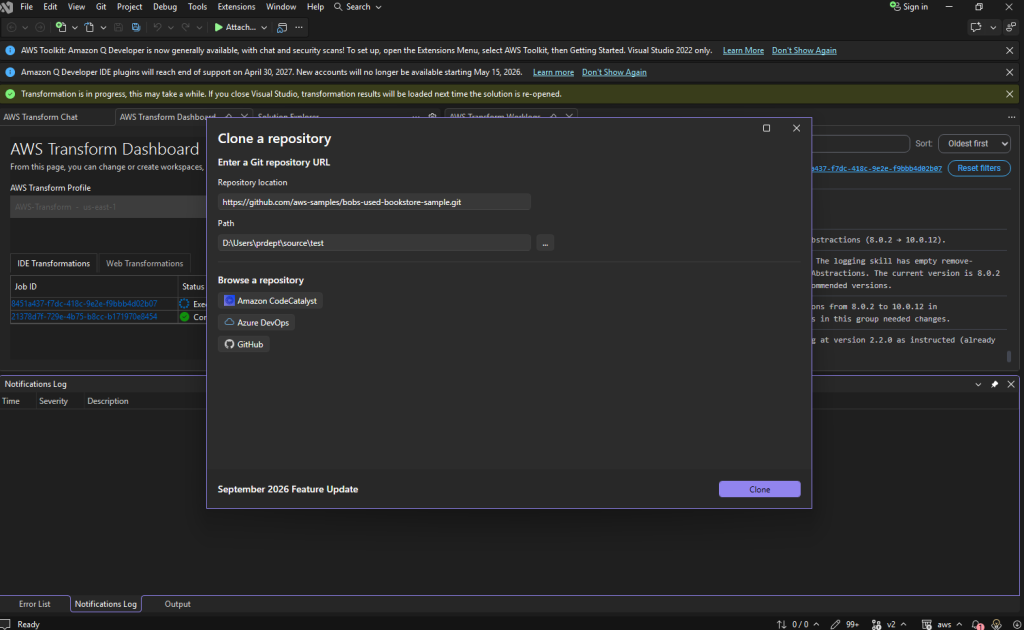
Screenshot of cloning a git repository in Visual Studio

Figure 2: Clone repository

  1. Select .NET version 8 or version 6 by following one of the options:
    1. Switch to a branch (.NET 8, e.g. v2).
      1. Click the branch name in the status bar at the bottom right, or open Git → Manage Branches.
      2. Under remotes/origin, right-click v2 and choose Checkout. Visual Studio creates a local v2 branch that tracks it.
    2. Switch to a tag (.NET 6, v1.12.0). Tags are harder to reach in the Visual Studio UI, so the Developer PowerShell is the simplest way using the following steps:
      1. Open View → Terminal, which is a Developer PowerShell with Visual Studio’s bundled git.
      2. Run: git checkout -b net6 v1.12.0 This creates a local branch net6 from the .NET 6 tag. Visual Studio will reload the solution.

Open your solution in Visual Studio, sign in to AWS Transform on the Getting Started panel (Extensions > AWS Toolkit > Getting Started), and confirm your region and workspace on the AWS Transform Dashboard. To initiate the transformation, select the solution in Solution Explorer and choose Port solution with AWS Transform from the context menu, then specify the target framework.
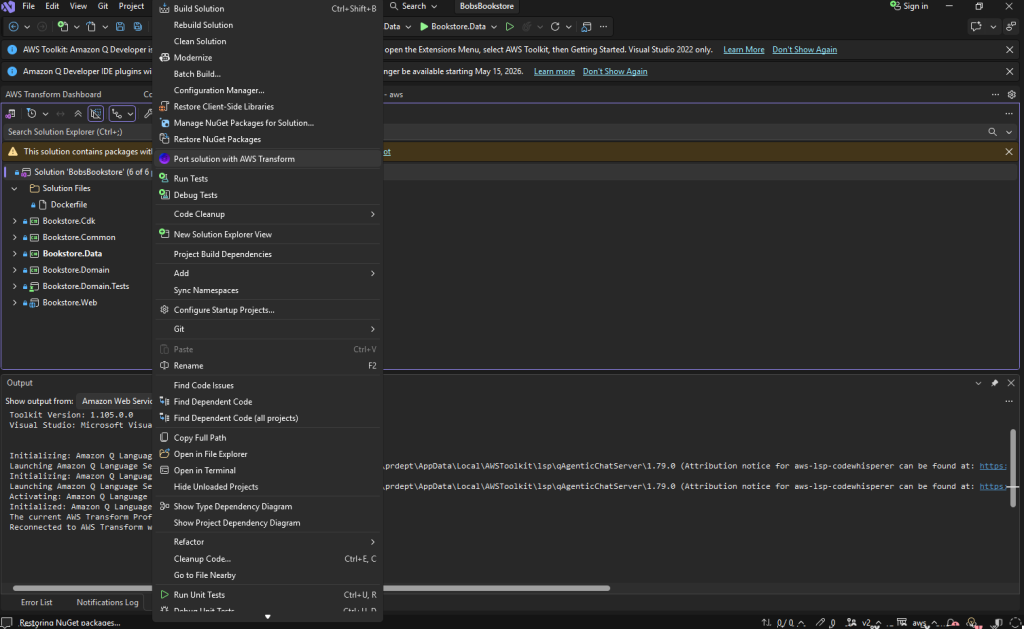
Screenshot of Visual Studio showing Solution Explorer context menu action to port solution with AWS Transform

Figure 3: Initiating a transformation job

This is the first decision point for tests. If you want to add unit test along with transformation, choose to generate unit tests at the start of the job. AWS Transform then assesses testability in parallel with the standard assessment, so by the time the transformation plan appears, the plan to cover the testable classes is already part of it. If you’d rather see the modernized code first, skip it here and enable it later — Step 4 covers that path.
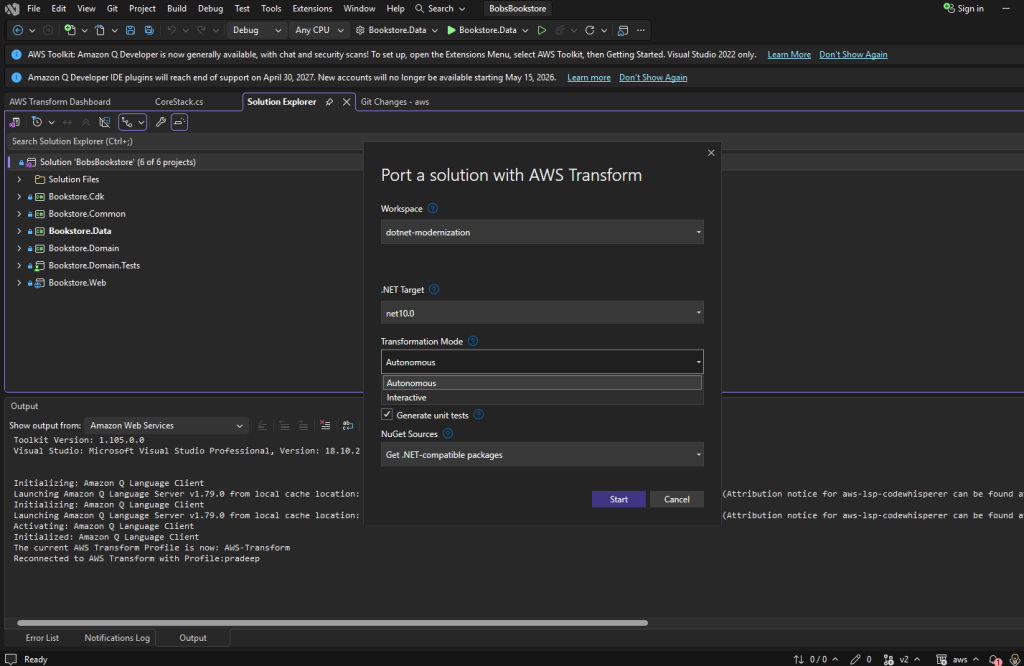
Screenshot of AWS Transform Port solution dialog in Visual Studio

Figure 4: AWS Transform dialog with Generate unit tests option

As with any AWS Transform job, you can choose interactive mode (the agent pauses for review and lets you steer) or autonomous mode (unattended, suitable for overnight jobs). Working interactively lets you see what the test agent proposes.

Step 2: Review the assessment

Once the job starts, the familiar windows open — Chat, Worklog, and Job Plan. When unit test generation is enabled at the start, the assessment shows up alongside the standard assessment summary in chat.

The agent focuses on the testable units and identifies the potential code for which unit test can be generated by analyzing the pre transformed code.

Step 3: Transform your projects

Approve the plan and let the agent transform the solution. The transformation itself proceeds exactly as it does without tests: projects are ported in dependency order, code changes are applied in Visual Studio automatically, and you can review diffs and ask the agent to explain any change. Because test generation was enabled at the start, the test project is populated as the corresponding production code is transformed, so tests arrive as part of the same job rather than as a separate follow-on effort.

Step 4: (Alternative) Enable unit test generation after transformation

If you didn’t opt in at the start — maybe to see the ported code before committing to tests — there’s no need to start over. Unit test generation is opt-in after transformation completes as well in the interactive mode. Once the transformation finishes and you’ve reviewed the modernized solution, ask the agent to generate unit tests. It runs the same testability assessment, plans coverage over the testable classes in the already-transformed code, and generates and validate the test code. This is the path to prefer when you want to eyeball the port first: transform, confirm the modernized code looks right, and then add the safety net.
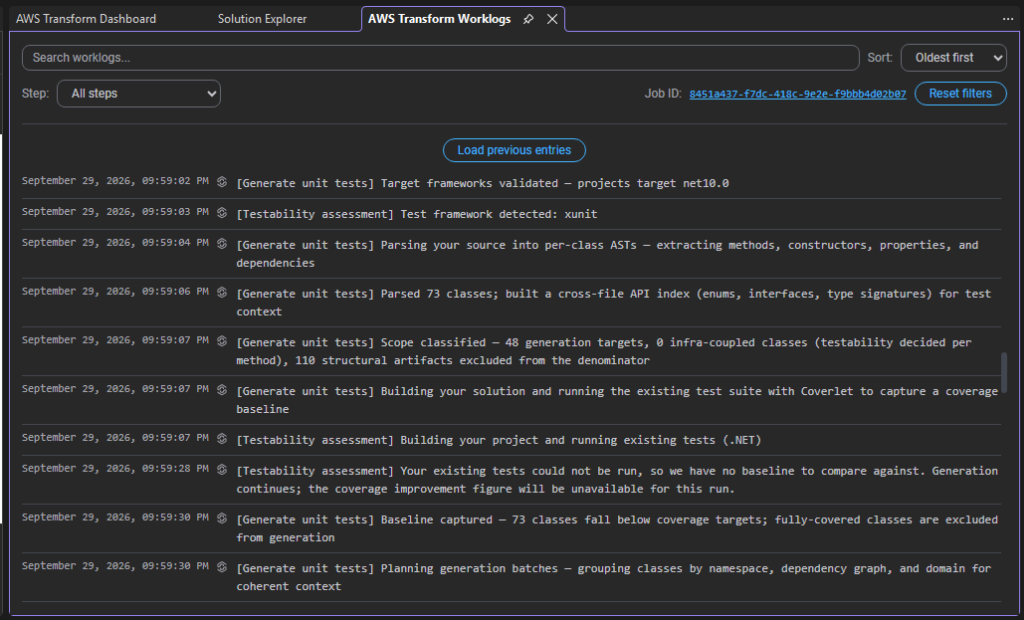
Screenshot of AWS Transform worklog window showing unit test activity

Figure 5: Worklog pane showing unit test generation

You can also view the status of unit test generation from the web console view of your job. Figure 6 shows 3 test projects were generated with 42 test files.
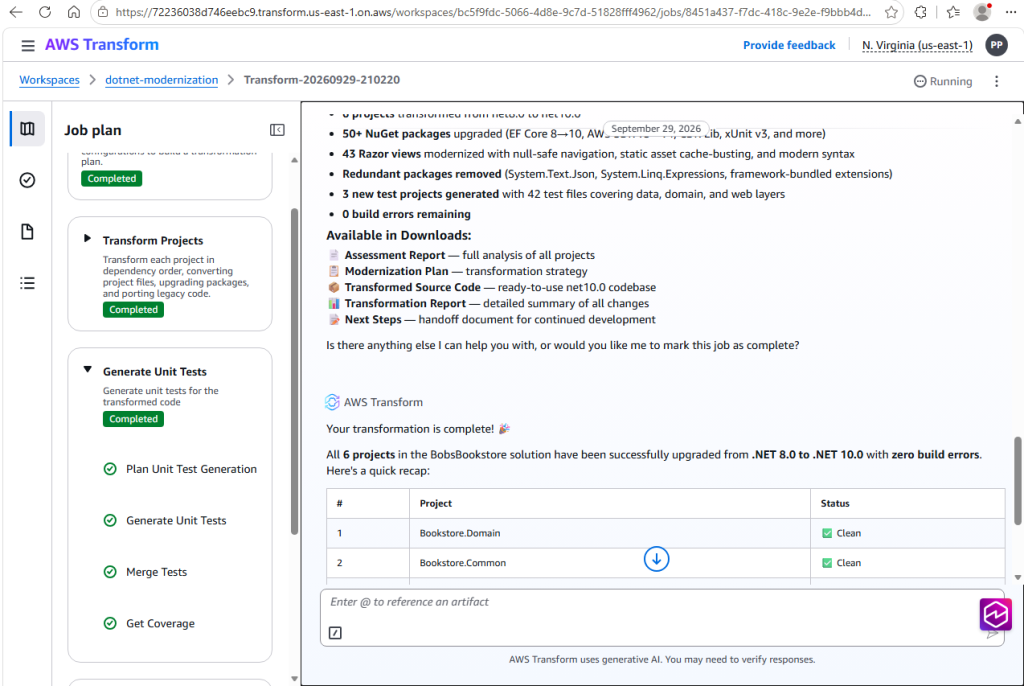
Screenshot of AWS Transform web console showing unit test activity

Figure 6: Web console view of job with unit test activity

Step 5: Review, Build and run the generated tests

The AWS Transform transformation report shows unit test results. Once Generate Unit test is complete, testable methods count, Line/Branch Coverage per project can be seen by selecting “Unit Test Generation” per project (Figure 7).
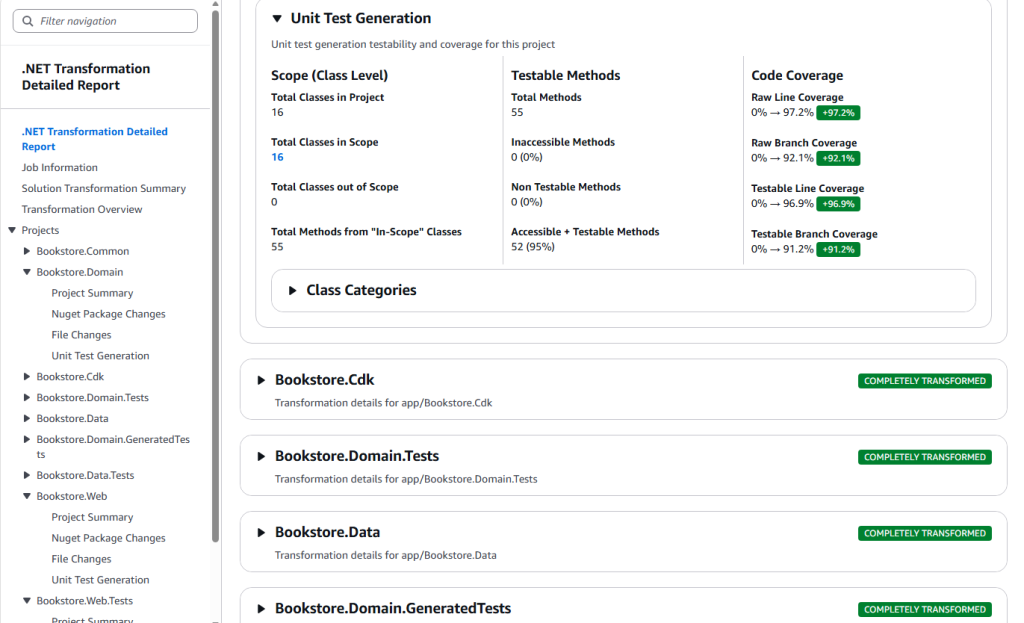
Screenshot of AWS Transform HTML transforamation report showing unit test generation details

Figure 7: Unit test generation results in transformation report

A summary of all the test across all projects can be seen under section “Unit Test Results” (Figure 8).
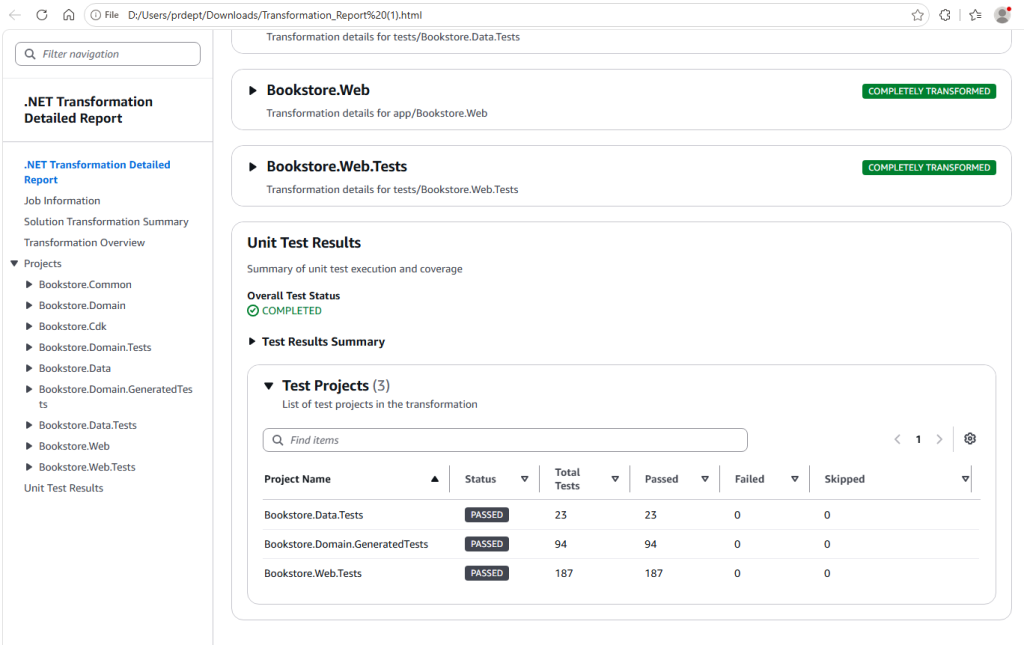
Screenshot of AWS Transform HTML transformation report showing unit test results

Figure 8: test results summary in transformation report

Conclusion

Modernizing a .NET Framework application has always produced a buildable codebase; what it hasn’t always produced is a way to maintain it with confidence. The generated Unit tests establish a coverage baseline on the modernized code so that every change made afterward can be checked by re-running the suite. With automatic unit test generation, AWS Transform for .NET provides that baseline as part of the modernization — assessing testability in parallel with the standard assessment, planning coverage over your testable classes, and generating the test code within the same job. Because it’s opt-in at either the start of a job or after transformation completes, you decide whether tests ride along with the modernization or get added once you’ve reviewed the port.

Try it on your next .NET modernization. Run a transformation with AWS Transform for .NET in Visual Studio, choose to generate unit tests, and finish the modernization with a maintenance safety net already in place for the changes that follow. To learn more, see Modernizing .NET in the IDE in the AWS Transform User Guide and the launch announcement.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Generate unit tests for your modernized code with AWS Transform for .NET”,
“datePublished”: “2026-10-05 20:03:00”,
“image”: “https://d2908q01vomqb2.cloudfront.net/b4c96d80854dd27e76d8cc9e21960eebda52e962/2026/10/05/generate-unit-tests-for-your-modernized-code-with-atx-net-1260×630.png”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://aws.amazon.com/blogs/dotnet/generate-unit-tests-for-your-modernized-code-with-aws-transform-for-net/”,
“mainEntityOfPage”: “https://aws.amazon.com/blogs/dotnet/generate-unit-tests-for-your-modernized-code-with-aws-transform-for-net/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}
AWS Continuum sets a new standard in autonomous code security

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: aws.amazon.com

As AI models become more capable, they uncover more security vulnerabilities and identify increasingly sophisticated paths to exploit them, raising the bar for how quickly defenders must respond. Security teams now face more potential vulnerabilities than their existing processes were designed to handle — each requiring investigation, reproduction, and a repair that must be tested to confirm it closes the vulnerability without breaking expected behavior.

AWS Continuum for code vulnerabilities accelerates this work with autonomous security at machine speed. To measure Continuum against a concrete public standard, we chose CyberGym-E2E, which asks an agent to find a vulnerability in a real codebase, demonstrate it with a working proof of concept, and repair it without breaking behavior covered by the project’s tests. Continuum passed 819 of 920 tasks within the benchmark’s 90-minute limit, achieving an 89.0% end-to-end success rate. This establishes a new standard 23.1 percentage points up from the previous public high of 65.9%.

Measuring the full vulnerability lifecycle

Many security benchmarks test a single task in isolation. Detection benchmarks test whether a system can identify suspicious code, while patching benchmarks begin with a known flaw and ask for a fix. CyberGym, the predecessor to CyberGym-E2E, also begins with a known vulnerability and focuses on exploit generation. By contrast, CyberGym-E2E evaluates the full vulnerability lifecycle, requiring a system to identify and demonstrate a vulnerability before producing a tested repair. This broader scope more closely reflects the work facing security teams.

Each CyberGym-E2E task places an agent in a container with a vulnerable revision of a real open-source project and the tools needed to build and test it. An agent can inspect and modify the source, but receives no vulnerability description, proof of concept, crash log, or original patch. External network access is blocked, and protected benchmark files cannot be modified. Within 90 minutes, the agent must submit an input demonstrating a vulnerability and a source-code patch. The full benchmark contains 920 tasks based on historical OSS-Fuzz vulnerabilities across 139 open-source projects. The median project contains more than 600,000 lines of code.

The benchmark evaluates each submission in four cumulative stages:

  1. S1 checks whether the agent produced an input that crashes the vulnerable program.
  2. S2 checks whether the agent’s patch prevents that crash.
  3. S3 checks whether the patched project still passes its functionality tests.
  4. S4 checks whether the patch also fixes the specific historical vulnerability selected by the benchmark.

CyberGym-E2E defines S3 as its main measure of end-to-end success. S4 is diagnostic because a repository may contain several valid vulnerabilities: an agent can find and repair a real flaw that differs from the benchmark’s selected target.

Continuum sets a new standard

Continuum for code vulnerabilities reached a new standard for every stage of CyberGym-E2E. The table below compares its performance with the previous best public results.

Stage

What it measures

Continuum

Previous public high

Difference

S1

Finds and reproduces a vulnerability

92.5%

67.9%

+24.6%

S2

Repairs its generated crash

89.6%

66.2%

+23.4%

S3

Preserves tested functionality

89.0%

65.9%

+23.1%

S4

Also repairs the benchmark’s selected vulnerability

37.8%

26.2%

+11.6%

On S3, the benchmark’s main measure of end-to-end success, Continuum passed 819 of 920 tasks. Its 89.0% success rate exceeds the previous public high of 65.9% by 23.1 percentage points. The result reflects both the capability of the underlying frontier models and Continuum’s design as a multi-agent security system. The next section examines how that system adds value beyond the models alone.

The official 89.0% result applies CyberGym-E2E’s 90-minute limit. When tasks were allowed to continue beyond that limit, Continuum’s end-to-end pass rate reached 93.7%, indicating higher potential coverage when longer-running analyses can complete.

We conducted the evaluation under CyberGym-E2E’s network-isolation and submission-review requirements. External retrieval was blocked during execution, and post-run trajectory review confirmed that successful results came from vulnerability analysis rather than retrieval of public historical fixes.

Harness design for end-to-end security

Continuum for code vulnerabilities is a multi-agent system organized around the main phases of the code vulnerability lifecycle: discovery, validation, and remediation. Each phase uses specialized agents adapted to the evidence and decisions it requires. The system carries evidence forward so that each phase builds on the work completed before it.

During discovery, Continuum analyzes the repository and develops candidate vulnerability findings. Its agents identify code paths that warrant deeper investigation and record the source evidence supporting each candidate.

During validation, specialized agents attempt to turn a candidate finding into a demonstrated security issue. They construct a proof of concept, run it against the vulnerable program, and determine whether the observed behavior supports the finding. This converts a potential code-level weakness into executable evidence.

During remediation, agents trace the vulnerability to its root cause and produce a patch. Continuum then verifies that the patch prevents the demonstrated failure and that the project’s functionality tests continue to pass. The repair is therefore evaluated against the same evidence used to establish the vulnerability.

Together, these phases create a connected record from suspicious code to a demonstrated vulnerability and tested repair. The architecture allows Continuum to adapt its tools, instructions, checks, and models to each phase while maintaining a consistent standard of evidence. It also supports a multi-model approach that can leverage complementary strengths and incorporate new models as they become available.

In customer environments, Continuum can also combine code-level evidence with available deployment context, including service exposure, network paths, permissions, and configuration. This context helps distinguish vulnerabilities with limited production impact from exposures that demand immediate action. CyberGym-E2E evaluates the code-level process but does not provide deployment context, placing this broader prioritization capability outside the benchmark’s scope.

CyberGym-E2E advances security evaluation by turning a complex, multi-stage process into a large public benchmark with reproducible tasks and outcomes that can be verified by running code. The CyberGym-E2E authors’ careful work on task construction, scoring, and submission standards gives the field a concrete foundation for measuring end-to-end progress.

To keep evaluation consistent and reproducible across 920 tasks, CyberGym-E2E focuses on memory-safety vulnerabilities in C and C++ projects. Sanitizer-detected crashes provide objective evidence of a defect, while subsequent checks determine whether a repair blocks the proof of concept and preserves functionality covered by the project’s tests. This design necessarily leaves many languages and vulnerability classes outside the benchmark’s current scope, including many of the most common and impactful bug classes observed in production systems. Evaluating these areas will require different task environments and equally rigorous forms of validation.

Our view of end-to-end security also extends beyond producing a tested code-level repair. In production systems, deployment context such as service exposure, network paths, permissions, and configuration often determines whether a vulnerability presents limited risk or demands immediate action. Future evaluations should test whether autonomous systems can reason about this context and prioritize findings according to their effect on the safety of the deployed system.

CyberGym-E2E’s value extends beyond the dataset itself. It makes the case that end-to-end security is worth defining and measuring as a task in its own right. That involves hard design choices about scope, evidence, and what counts as success, and CyberGym-E2E gives the field a concrete starting point for working through those choices. This system-level view complements our work on the Deception Benchmark, which evaluates a narrower but related capability: how reliably individual frontier models distinguish real vulnerabilities from safe code. Together, they examine security performance at both the model and system levels.

To learn how AWS Continuum for code vulnerabilities helps teams discover, validate, prioritize, and remediate vulnerabilities at machine speed, visit the AWS Continuum product page.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “AWS Continuum sets a new standard in autonomous code security”,
“datePublished”: “2026-10-05 21:41:00”,
“image”: “https://d2908q01vomqb2.cloudfront.net/22d200f8670dbdb3e253a90eee5098477c95c23d/2026/05/05/aws_logo.jpg”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://aws.amazon.com/blogs/security/aws-continuum-sets-a-new-standard-in-autonomous-code-security/”,
“mainEntityOfPage”: “https://aws.amazon.com/blogs/security/aws-continuum-sets-a-new-standard-in-autonomous-code-security/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}
Asos Shares Plunge Following Public Data Breach Threat

0

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: wwd.com

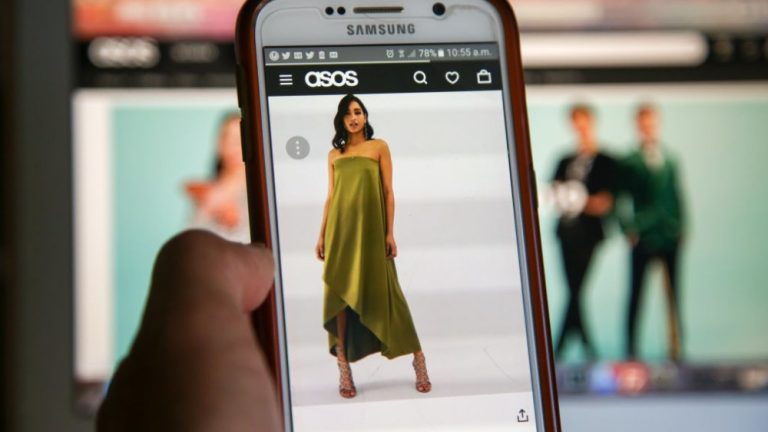
Hackers sent a threat to Asos that was heard loud and clear — by both its users and investors.

Shares of Asos were down more than 11 percent to 445.90 pence in midday trading as stockholders tried to gauge the fall out of an unusual and highly visible security breach.

The company was not immediately available for comment, but shoppers who use the app were posting screenshots of a push alert they received that looked like an attempt at blackmail.

“Dear Asos DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it,” the alert read, calling out the company’s data protection officer and tech specialists and apparently referring to Snowflake, the cloud-based data storage company.

Threats against online retailers are nothing new, but they usually happen away from the consumer eye. It is very unusual for app users to have the push-alert function co-opted on their phones, putting average consumers in the middle of the crossfire.

Although many of the details are still not known, the hack looks like something of a parable for fashion in the digital age, especially with AI supercharging the ability to break into systems that were seen as secure.

Even if the hackers have nothing else but the ability to trigger a push alert to Asos app users, that in itself is the ability to disrupt the all-important relationship with the shopper.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Asos Shares Plunge Following Public Data Breach Threat”,
“datePublished”: “2026-10-06 14:41:00”,
“image”: “https://wwd.com/wp-content/uploads/2024/03/AsosMobileApp.jpg?crop=0px%2C55px%2C1024px%2C573px&resize=1000%2C563”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://wwd.com/business-news/technology/asos-shares-drop-public-hack-alert-1239315437/”,
“mainEntityOfPage”: “https://wwd.com/business-news/technology/asos-shares-drop-public-hack-alert-1239315437/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}
Azure Standard founder pens new book, stays true to farm roots

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: capitalpress.com

Azure Standard founder pens new book, stays true to farm roots

Published 7:30 am Tuesday, October 6, 2026

Founder and CEO wants to encourage farmers, those with health issues

DUFUR, Ore. — This small town, population 650, holds the headquarters for an organic and natural foods distributor with 500 farm partners around the world and deliveries to 100,000 customers across the U.S. every month.

“I don’t think very many local people know how big we are,” said David Stelzer, founder and CEO of Azure Standard, which sprang from his family’s wheat farm nearly 40 years ago.

Stelzer’s new book, “Seeds of Hope: The Azure Standard Story,” will be released Oct. 13.

He started writing to encourage people with health issues and fellow farmers feeling stuck in their practices or commodity markets.

“You can win, but think outside the box,” Stelzer said.

He succeeded with direct marketing and value-added products.

The book also details challenges such as an IRS raid at the family farm, a devastating fire that destroyed a warehouse and a battle over weeds with Sherman County, which wanted to spray Azure’s organic acreage.

Stelzer wrote that a social media campaign, which flooded the county with phone calls and emails, forced officials to find a reasonable solution.

More room for growth

Stelzer said Azure stayed true to its roots as it scaled up from a single delivery van.

In the 1980s, he delivered his family’s wheat to Northwest health food stores and cooperatives.

Stelzer saw a need and refocused on distribution, but home deliveries quickly became too time-consuming so he established community drop locations.

Azure now has 5,000 sites throughout the U.S.

While most sales are online, the business still has a call center and paper catalog.

Stelzer said there’s more room for growth.

“The demand for high quality organic food is through the roof,” Stelzer said.

The pandemic boosted demand with Americans cooking more at home and wanting better options, said Crystal Stelzer, Stelzer’s daughter and Azure’s bakery manager.

An explosion of orders put Azure on solid financial footing and led to expansion.

The business more than tripled its employees to 550 in a few years.

That includes 70 in Dufur — where the business operates a bakery, grocery store, hardware store and gas station — and 150 distribution center employees in nearby Sherman County.

Azure is building a processing center for value-added products outside Dufur and the facility will include an individual quick freeze plant.

The business also has customer service, warehouse and delivery workers throughout the country.

A mission to create quality food

Azure Standard started, in a way, because Stelzer was constantly sick as a boy.

A naturopath convinced his parents to change their diet to natural foods.

Stelzer’s health returned and his father committed to organic farming in the 1970s.

From one generation to the next, the family’s health changed dramatically. Stelzer said his 11 children only had one doctor visit growing up, for a broken bone.

“I want to create hope that we can change the trajectory of the health of our families, because it changed for my family,” he said.

“My whole mission is to connect farmers who produce quality food with consumers,” Stelzer added.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Azure Standard founder pens new book, stays true to farm roots”,
“datePublished”: “2026-10-06 14:36:00”,
“image”: “https://capitalpress.com/wp-content/uploads/sites/11/2026/10/news_azure_100926_cap_01.jpeg”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://capitalpress.com/2026/10/06/azure-standard-founder-pens-new-book-stays-true-to-farm-roots/”,
“mainEntityOfPage”: “https://capitalpress.com/2026/10/06/azure-standard-founder-pens-new-book-stays-true-to-farm-roots/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}
Zylo Ushers in a New Era of Agentic SaaS Management

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: aithority.com

General availability for Zylo Clarity AI marks a new phase of agentic SaaS Management, as growing adoption of the Zylo MCP Server expands what enterprises can accomplish at scale

Zylo, the enterprise leader in SaaS and AI spend optimization, today announced the general availability of Zylo Clarity AI, its SaaS Management agent embedded directly in Zylo’s platform. Teams can ask Clarity to uncover unused licenses, prepare for renewals, update portfolio records at scale, and build and run workflows directly from a plain-language request.

Zylo has spent nearly a decade building the trusted system of record enterprises rely on to manage software. That foundation now powers an agentic system of action, drawing on over $100 billion in SaaS, cloud, and AI spend data and a decade of SaaS Management expertise.

“For years, SaaS Management has given enterprises the visibility and intelligence to find savings and optimization opportunities across their software portfolios,” said Ben Pippenger, Co-founder and VP of Strategic Partnerships at Zylo. “Agents change what enterprises can do with that intelligence, reducing the resources required to drive outcomes and opening up savings and optimization across the portfolio at an entirely new scale.”

Also Read: AiThority Interview with Gou Rao, co-founder and CEO at NeuBird AI

Zylo Clarity Brings Agentic SaaS Management to Every Client

First introduced in May, Zylo Clarity AI is now generally available to all Zylo users.

Clarity plans the steps needed to complete a request and calls the appropriate Zylo tools to execute them, adapting its approach as results come back. Built-in controls allow people to review and approve consequential actions before they are taken.

Making Zylo Agent-Ready Across the Enterprise

Zylo is bringing agentic SaaS Management wherever enterprises choose to build their agents. While Clarity puts an agent directly inside the platform, the Zylo Model Context Protocol (MCP) Server makes Zylo agent-ready across the enterprise, extending its data, intelligence, and actions to AI tools including Claude, ChatGPT, and Gemini.

Through MCP, Zylo becomes a data and action layer for enterprise agents, giving them access to live spend, contract, and usage data and enabling agentic workflows that extend across other MCP-enabled systems. Usage of the Zylo MCP Server has nearly tripled within Zylo’s client base since early August, with enterprises building SaaS Management directly into their agents and AI workflows.

Zylo continues to expand the foundation for agentic SaaS Management across Clarity, MCP, and its API. Workflows, automations, Activity History, and enhanced Custom Field capabilities are now available across all three, while new Company Context allows administrators to provide company-specific context for Clarity and MCP users.

Zylo’s agentic innovation comes as AI transforms both how enterprises manage software and the spend they need to manage. On October 29, Zylo will host the AI Spend Summit, a virtual event convening industry leaders to explore what it takes to manage AI costs at scale, with Zylo unveiling a new AI spend management solution as part of the program. To learn more and register, visit zylo.ai.

Also Read: ​​AI and The Future of Work: Artificial Intelligence Is Expanding Organizational Intelligence Beyond Human Limits

[To share your insights with us, please write to [email protected] ]

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Zylo Ushers in a New Era of Agentic SaaS Management”,
“datePublished”: “2026-10-06 14:21:00”,
“image”: “https://aithority.com/wp-content/uploads/2026/10/automation-industry-3d-rendering.jpg”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://aithority.com/saas/zylo-ushers-in-a-new-era-of-agentic-saas-management/”,
“mainEntityOfPage”: “https://aithority.com/saas/zylo-ushers-in-a-new-era-of-agentic-saas-management/”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}
Senator Collins Receives 2026 Clean Energy Champion Award

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: barharborstory.substack.com

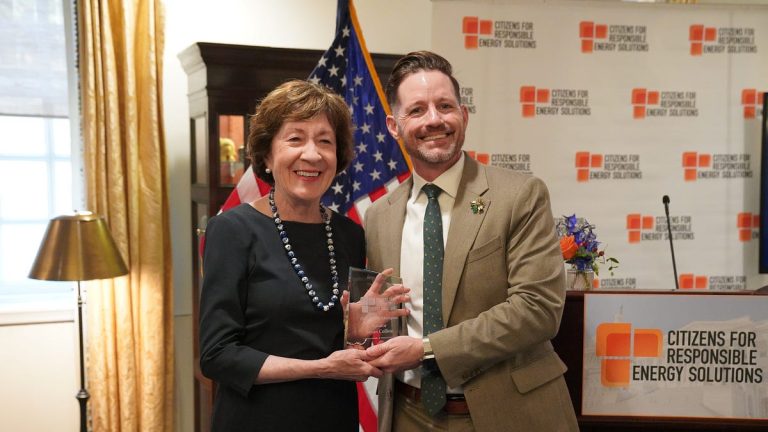
WASHINGTON, D.C. – U.S. Senator Susan Collins was named a 2026 Clean Energy Champion by Citizens for Responsible Energy Solutions (CRES). CRES recognized Senator Collins for her longstanding work to strengthen grid resilience, advance energy storage and clean energy technologies, and support investments in the nation’s energy infrastructure.

“CRES has been an important partner in advancing responsible energy policies that strengthen our nation’s economy and energy security, and I am grateful to be recognized by the organization as a Clean Energy Champion,” said Senator Collins. “As Chair of the Senate Appropriations Committee, I will continue working across the aisle to advance an all-of-the-above energy strategy that helps make energy more reliable and affordable while encouraging American innovation.”

Senator Collins was a member of the bipartisan group of ten senators who negotiated the 2021 Infrastructure Investment and Jobs Act, which established the Grid Resilience and Innovation Partnerships (GRIP) grant program to strengthen and modernize the nation’s electric grid. Through the GRIP program, Form Energy received a nearly $150 million federal award for a new battery-based energy storage facility located at the site of the former Lincoln Paper & Tissue Mill. In August, Senator Collins joined U.S. Secretary of Energy Chris Wright and local leaders in Lincoln to discuss the plans for the new facility.

The Better Energy Storage Technology (BEST) Act, bipartisan legislation authored by Senator Collins to support grid-scale energy storage research and development and improve the efficiency of the nation’s electric grid, was signed into law in 2020.

Share

Leave a comment

Webinar explores digital banking platform chang…

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: pluang.com

Uber buys ezCater for $2.3B to expand into catering services via Uber Eats

Uber is acquiring ezCater, a leading U.S. catering platform, for $2.3 billion in cash to expand its Uber Eats offerings into large-scale catering and workplace meals. ezCater, founded in 2007, has generated over $2.5 billion in gross bookings in the …

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Webinar explores digital banking platform chang…”,
“datePublished”: “2026-10-06 14:15:00”,
“image”: “https://image-cdn.pluang.com/web/news-cards/v2/GSS/41b04736981190ba1d205eca44d3581e2dc2569b8cc6c487ba8a61c3f5db8e68-en.webp”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://pluang.com/en/news-feed/alkami-bawa-keahlian-implementasi-ke-keputusan-digital-banking-tetap-atau”,
“mainEntityOfPage”: “https://pluang.com/en/news-feed/alkami-bawa-keahlian-implementasi-ke-keputusan-digital-banking-tetap-atau”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}
‘Below’: When to Watch Josh Hartnett Battle a Mysterious Sea Creature on Netflix

0
Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.cnet.com

Move over, Widow’s Bay — there’s a new seaside horror show in town. Below is the name of the program in question, and by the looks of things, the upcoming series will be less comedic than Apple TV’s Emmy-winning show and more atmospheric, like the numerous shows Mike Flanagan created for Netflix.

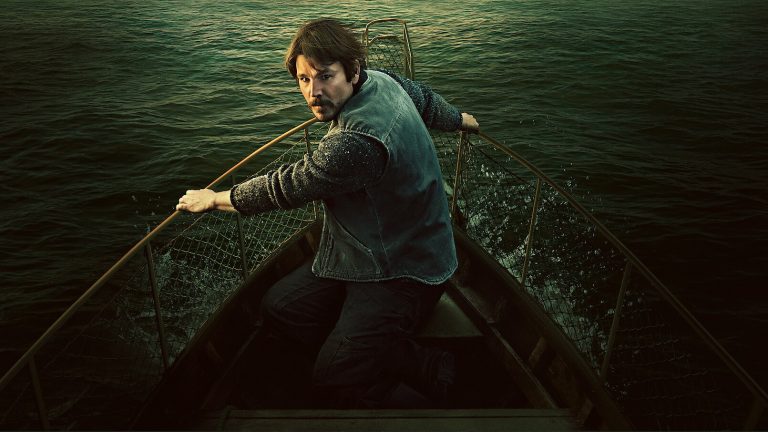
Below stars Josh Hartnett as a Newfoundland fisherman named Calvin Penney who gets involved with a growing mystery impacting his home: Something dangerous is in the water, and it’s not going away. Is it a sea monster of the Loch Ness variety? That’s unknown at this time, but something tells me this creature isn’t like anything Penney or his tight-knit community have dealt with before.

Starring opposite Hartnett are Stranger Things alum Charlie Heaton, Mackenzie Davis, Willow Kean, Ruby Stokes, Rohan Campbell and Kaleb Horn. The program hails from creator Jesse McKeown, who most recently served as a writer on The Umbrella Academy.

Read on for more information on when to stream Below on Netflix.

Read more: 15 of the Best Horror Movies to Watch on Netflix Right Now/

When to watch season 1 of Below on Netflix

All six episodes of Below will rise to the surface on Netflix all at once on Thursday.

Netflix offers three different subscription plans to choose from. If you’re fine with commercials, you can opt for the Standard with Ads plan for $9 per month. The Standard plan costs $20 per month. For Premium, your out-of-pocket cost would be $27 per month. For more information on the streamer, check out our in-depth review.

Aaron is a writer for the streaming entertainment team. Previously, he wrote about TV and movies for places like Rotten Tomatoes, Inverse, TheWrap, Washington Post and The Hollywood Reporter. Aaron is also an actor and played a nerd on TV a lot in the ’90s. Seriously.

See full bio

CrowdStrike Launches Fourth Cybersecurity Startup Accelerator With AWS and Nvidia

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: finance.yahoo.com

Cybersecurity ©Peachaya Tanomsup

CrowdStrike (NASDAQ:CRWD) has announced the fourth edition of its annual Cybersecurity Startup Accelerator in partnership with Amazon Web Services (AWS) (NASDAQ:AMZN) and Nvidia (NASDAQ:NVDA).

Applications are open globally until November 2, 2026, with the eight-week programme scheduled to run from January 11 through March 8, 2027.

The accelerator is designed to connect early-stage cybersecurity companies with technical and business representatives from CrowdStrike, AWS and Nvidia. Up to 10 finalists are expected to pitch at RSAC 2027, scheduled for April 5-8, where one winner will be selected.

Participating companies may also be considered for investment from the CrowdStrike Falcon Fund.

Accelerator Adds CrowdStrike Falcon Development Tools

This year’s programme will provide participating startups with access to CrowdStrike’s Falcon Foundry agent development tools and Falcon APIs.

Participants will also be able to develop verified integrations and potentially publish their products through the CrowdStrike Marketplace.

AWS is expanding its go-to-market support through AWS Partner Network onboarding, technical validation and AWS Marketplace listings. Nvidia will provide technical training and developer resources through its Nvidia Inception programme.

“Together with AWS and Nvidia, we’re putting the scale and power of our companies and ecosystems behind the best founders to help them build faster, reach more customers, and grow,” said Daniel Bernard, chief business officer at CrowdStrike.

CrowdStrike Says Accelerator Has Supported More Than 90 Startups

According to CrowdStrike, the accelerator has supported more than 90 startups globally, with participating companies collectively raising nearly $1 billion in funding.

Previous participants include Onum, which was subsequently acquired by CrowdStrike, as well as Terra Security and Remedio, which raised $38 million and $65 million, respectively. Another previous participant, Fabrix Security, was acquired by Silverfort.

CrowdStrike also said last year’s accelerator winner, Jazz, reported that its revenue nearly tripled and its pipeline increased tenfold following the programme. These figures represent company-reported results and do not establish that the accelerator was solely responsible for the changes.

CJ Moses, chief information security officer at Amazon, said the programme gives founders access to cloud infrastructure and technical expertise to develop products for enterprise customers.

Saša Zdjelar, chief security officer at Nvidia, said participants will have access to accelerated computing and artificial intelligence technologies through the programme.

Crowdstrike stock price

Amazon stock price

Nvidia stock price

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “CrowdStrike Launches Fourth Cybersecurity Startup Accelerator With AWS and Nvidia”,
“datePublished”: “2026-10-06 12:51:00”,
“image”: “https://s.yimg.com/lo/mysterio/api/5cfa7468772880e0564b1130ebff9f9971a9f2894a703f6ba243d09db6493862/lightyear_networkapi/resizefill_w1200%3Bquality_80%3Bformat_webp/https%3A%2F%2Fmedia.zenfs.com%2Fen%2Finvestorshub_458%2F76b7b8d46a608a3e9d3c0a88e760b294.png”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://finance.yahoo.com/technology/articles/crowdstrike-launches-fourth-cybersecurity-startup-125113629.html”,
“mainEntityOfPage”: “https://finance.yahoo.com/technology/articles/crowdstrike-launches-fourth-cybersecurity-startup-125113629.html”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}
Cybersecurity Budgets Tighten, Change As AI Adoption Continues

0

Editorial Disclosure: This article is an editorial-assisted curated synthesis of verified global coverage. The original source reporting has been analyzed, structured, and compiled by Pune.Media’s Editorial Desk to bring you high-density business insights.

Original Coverage & Source Attribution: www.dice.com

Even with artificial intelligence spending expected to reach into the trillions, those dollars are not filtering down to internal cybersecurity teams as quickly. Security budgets are expected to grow by an average of 5 percent in 2026, compared with 4 percent last year, according to a recent survey of industry leaders.

At the same time, 55 percent of CISOs report flat or declining budgets this year. While nearly seven out of 10 security leaders noted that AI is a major priority for new budgets heading into 2027, AI alone accounts for about 3 percent of security spending, while software and AI combined represent 35 percent of the security budget – about two percentage points behind staff and compensation.

Additionally, about 38 percent of organizations fund AI security outside the security budget through areas such as IT, data or innovation, according to the report published by cyber-risk consulting company IANS Research and recruiting firm Artico Search. The data includes responses from 500 CISOs and security leaders from interviews conducted between April and August.

The research suggests that while overall AI spending is still increasing, some of the capabilities CISOs and their internal security teams are using are coming from other budgets within their organizations. This trend could change how security leaders approach their budgets in 2027 and beyond, especially as cybersecurity teams are increasingly tasked with securing these AI technologies and assessing risk.

“Another implication of investing in emerging technologies is that security is gaining tailwinds from other investments in AI and broader technology, meaning some security capabilities are particularly funded out of someone else’s budget,” Steve Martano, IANS Faculty and partner in Artico Search’s cyber practice, noted in the report.

An uncertain economy is also driving tighter evaluations of cybersecurity return on investment, as well as greater scrutiny of security spending, including hiring and recruiting talent, said Robb Reck, chief information, trust and security officer at Pax8.

“Rather than expanding teams, organizations today are looking to AI to increase their existing workforce’s effectiveness. Still, leaders need to remain careful, continuing to gauge how AI adoption will ultimately affect team dynamics and resource needs,” Reck told Dice.

Budgeting Cybersecurity in an AI World

As AI spending becomes an increasingly pressing priority, CISOs and internal security teams face three pressure points in their cybersecurity budgets, said Collin Hogue-Spears, senior director of solution management at security firm Black Duck. These include:

  • The first is pressure from the board, which mandates that enterprise AI is already a top CEO priority. Security then gets its budget because nobody can defend the rest of the program without it.
  • The second pressure point is capacity. Alert backlogs and unfilled seats were constraints before AI arrived, so teams buy the throughput they cannot hire for.
  • The third is the attacker-side clock. Since the board believes the other side already has the tool, a matching purchase needs no ROI model. That means AI becomes an arms-race purchase rather than a capital-budget purchase.

This also means developing new budget proposals that document how AI agents work and what it takes to secure them, as well as how they affect the rest of the organization.

“Security leaders must price the work the model actually does. Hold back a set of alerts the model never sees, then compare: what did each correctly closed alert cost, and how often was the auto-close right? Run a board slide that turns a quiet quarter into a win for the model and the first auditor who asks for the comparison group takes it apart,” Hogue-Spears told Dice. “Measure what the model closed, not what the quarter avoided.”

Some of today’s largest cybersecurity expenditures are coming from investments in application security, security operations and AI usage governance, principally driven by automated code patching and the need to protect corporate models from data leakage.

At the same time, dedicated budgets are increasingly carved directly out of existing money earmarked for Security Operations Centers (SOCs) and legacy automation allocations to help fund the so-called “token budgets” and autonomous agentic tools, said Acalvio CEO Ram Varadarajan.

In many cases, fear of a data breach or attack is driving spending, and CISOs might see AI as a way to offset those concerns.

“Fear asymmetry drives the spend. If a missed breach is visible and career-ending, buying ‘AI-powered’ security is blame insurance, not a validated bet,” Varadarajan told Dice. “Sell to that fear, and once ‘AI’ becomes the market’s baseline expectation, peer-following procurement replaces evidence-based procurement, which explains why the most popular use cases aren’t the best-performing ones.”

AI ROI, however, is harder to measure because CISOs and security teams are pricing the absence of a rare, adversarial event, not counting throughput.

“A quiet quarter could mean the tool works, or that attackers just haven’t tried yet, and against a live, adapting adversary, there’s no clean control group to prove,” Varadarajan added.

For many CISOs, spending on AI tools and platforms to help with cybersecurity, even as budgets stagnate or only increase marginally, is seen as a necessary way to stay ahead of current trends and avoid falling behind.

“We’ve learned lessons from the past of trying to ‘bolt’ security onto technology adoption, so many security leaders are rightfully trying to be early and secure the adoption of this technology at the earliest possible aspects of the lifecycle as they can,” Chris Hughes, vice president of security strategy at Noma Security, told Dice. “They also do not want to be caught flat-footed with the board or executive leadership when they are asked what their AI security strategy is, especially among all the FUD and hype around AI and cyber, agent breakouts, cyber risks, and widespread AI-driven vulnerability discovery that has broken into the mainstream narrative beyond cyber circles.”

Security Budgets and Hiring

The pressure to do more with existing cybersecurity budgets is also reshaping the security workforce. While organizations are not broadly cutting security positions because of AI, they are changing the skills they seek, with greater demand for professionals who can apply AI to cybersecurity work.

The IANS and Artico data show that while cybersecurity budgets are flat – which can also affect decisions on talent recruitment, hiring and retention – AI is not taking cybersecurity professionals’ jobs. About 75 percent of respondents noted they didn’t anticipate cutting positions on their security teams due to AI adoption.

The results also reinforced two other trends for cybersecurity professionals: Entry-level jobs are being automated, and organizations are looking for security pros – even in mid-level roles – with AI skills.

“Demand is shifting toward people with deeper security, AI and business judgment, while entry-level roles are being reduced or redesigned. That is unfortunate, because the routine work AI absorbs is also where people build institutional knowledge and become experienced defenders,” Mika Aalto, co-founder and CEO at Hoxhunt, observed. “At the same time, every AI agent we connect to internal systems is effectively a synthetic employee, and if it is mistaken or compromised, it can become an insider threat operating at machine speed.”

Pax8’s Reck also noted that cybersecurity professionals who use AI to augment their work can create a better understanding of how these virtual chatbots and agents work, which makes them more valuable even as budgets for hiring stay flat.

“Security professionals who treat AI as something that will amplify their work, rather than threaten it, are the ones landing roles, even with tighter security budgets,” he added.

{
“@context”: “https://schema.org”,
“@type”: “NewsArticle”,
“headline”: “Cybersecurity Budgets Tighten, Change As AI Adoption Continues”,
“datePublished”: “2026-10-06 06:00:00”,
“image”: “https://www.dice.com/binaries/large/content/gallery/dice/insights/2024/08/adobestock_797202412.jpeg”,
“author”: {
“@type”: “Organization”,
“name”: “Pune.Media Editorial Desk”,
“url”: “https://pune.media”
},
“publisher”: {
“@type”: “Organization”,
“name”: “Pune.Media”,
“logo”: {
“@type”: “ImageObject”,
“url”: “https://pune.media/wp-content/uploads/logo.png”
}
},
“isBasedOn”: “https://www.dice.com/career-advice/cybersecurity-budgets-tighten-change-as-ai-adoption-continues”,
“mainEntityOfPage”: “https://www.dice.com/career-advice/cybersecurity-budgets-tighten-change-as-ai-adoption-continues”,
“creativeWorkStatus”: “Editorial-assisted Curation”,
“comment”: {
“@type”: “Comment”,
“text”: “This article was curated, verified, and structured under organizational human editorial guidelines by the Pune.Media Editorial Desk.”
}
}
