Original Coverage & Source Attribution: www.vietnam.vn
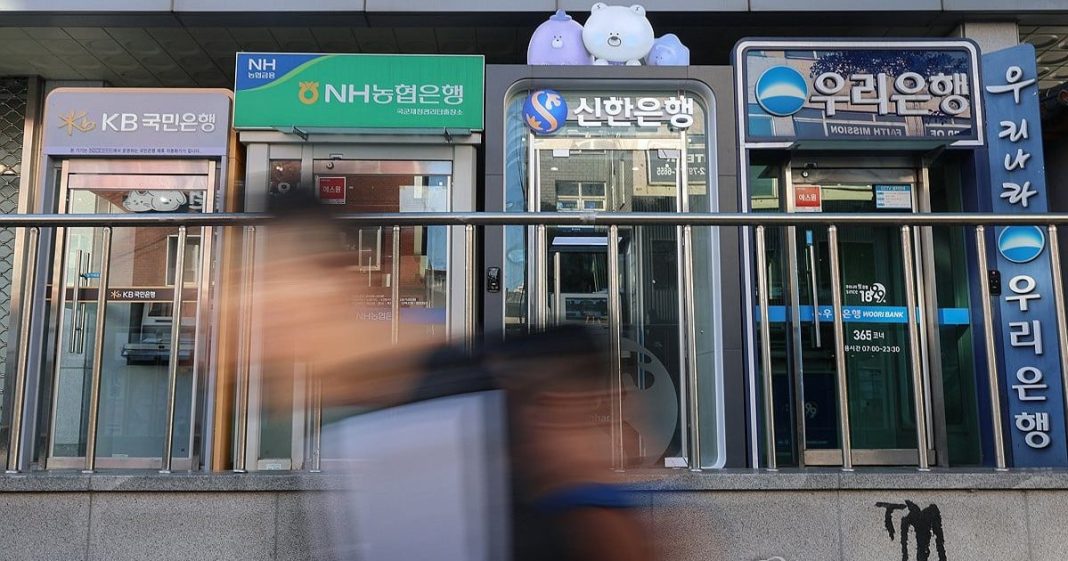
Numerous banks in South Korea were subjected to cyberattacks – Photo: ATMs of various banks located in central Seoul (Source: Yonhap)
AI can help hackers scale up their attacks.
In South Korea, a number of banks have been targeted by cyberattacks. Notably, Shinhan Bank announced on October 1st that the information of approximately 25,000 customers had been compromised, including names, phone numbers, annual income, and loan limits.
According to Yonhap News, experts suspect that AI agents were used to exploit vulnerabilities and illegally infiltrate a service used by loan recruiters.
As of October 8th, cybersecurity firm CrowdStrike announced that it had identified a potential suspect behind attacks targeting at least nine South Korean banks. According to CrowdStrike, the suspect used the ARTEX AI engine along with several large language models to aid the attack; some operations were carried out via Claude Code. South Korean police are continuing their investigation into the matter.
ARTEX was originally an open-source tool for assessing security risks. After reports emerged that the tool was being exploited to attack banks, the developers shut down the source code and removed the ARTEX GitHub page.
According to Mun Chong-hyun, director of cybersecurity company Genians, AI tools developed for defensive purposes can become a “double-edged sword” when used to aid criminal activity.
Besides Shinhan, KB Kookmin Bank and Hana Bank also announced data leaks affecting 119 and 89 customers, respectively. South Korean financial regulators have stepped up inspections and are working with banks to respond.
Experts warn that when personal and financial data are stolen simultaneously, AI generation can be exploited to create personalized scam scenarios, making them harder for recipients to detect.
In Japan , the situation is also becoming alarming. On October 9th, the government warned ministries, local authorities, and businesses to increase vigilance against increasingly sophisticated cyberattacks.
According to cybersecurity firm Macnica, the number of website attacks aimed at stealing personal information reported in Japan has increased from an average of 6 incidents per month in the first half of the year to 23 incidents per month since July. Experts believe that AI may be being used by hackers to detect vulnerabilities and deploy attacks more quickly.
A series of major incidents have been announced. The ride-sharing service Times Car reported that approximately 6.6 million member accounts were affected, with about 1.6 million accounts having their identity verification documents accessed, including driver’s license photos and other papers. MrMax Holdings confirmed that the information of up to 1.735 million members was leaked following an unauthorized access attempt. Meanwhile, the survey website infoQ, operated by a subsidiary of GMO Research & AI, was also accessed illegally, with up to 948,498 instances of personal data potentially being compromised.
Notably, according to Professor Yoshioka Katsunari of Yokohama National University, the average time from when a vulnerability is disclosed to when an actual attack occurs has decreased from 141 days in 2024 to 35 days by the end of August 2026.
Meanwhile, a survey of IT trends among Japanese businesses revealed that about three-quarters of companies with revenues of 100 billion yen or more admitted to a shortage of personnel specializing in cybersecurity and network security.
In response to this situation, the Japanese government is strengthening cooperation with businesses and advising citizens to use multi-factor authentication, avoid sharing passwords, and be wary of suspicious messages.
AI agents are placing new demands on accountability and security.
Beyond being exploited as attack tools, AI agents capable of autonomously performing tasks are also raising new issues regarding access control and accountability in the event of incidents.
In Australia, an OpenAI AI agent illegally accessed the government’s health statistics data portal in June while conducting research. OpenAI stated that no patient records or personal financial information were accessed, but the company only notified the Australian government in September.
On October 6th, at a hearing in the Australian Parliament , representatives from OpenAI and Anthropic stated their support for regulations mandating the reporting of data breaches caused by AI agents, rather than leaving it up to businesses to decide whether or not to disclose the information.
Against this backdrop, the AI security market is projected to grow rapidly. According to Gartner, global information security spending is expected to reach approximately $244 billion in 2026. The market for protecting AI systems (securing AI) alone is projected to reach approximately $2.835 billion in 2026, an 83% increase; nearly $4.8 billion in 2027; and $7.7 billion in 2028.
Gartner also predicts that by 2029, more than half of successful attacks targeting AI agents could exploit weaknesses in access control or malicious prompt injection techniques.
Interest in this sector is also reflected in investment flows. In the third quarter of 2026, global venture capital investment in cybersecurity reached approximately $5.26 billion, with Israeli startups raising at least $2.425 billion, equivalent to nearly half of the total global investment.
Countries are strengthening AI risk management.
Along with cybersecurity challenges, the rapid development of AI is prompting countries to refine their legal frameworks for regulating this technology.
In Southeast Asia, Malaysia is developing a comprehensive AI law that adopts a risk-based approach, replacing the previous voluntary guidelines.
Malaysian Digital Minister Gobind Singh Deo said on October 5 that the government is studying enforcement mechanisms to regulate AI. Previously, the National AI Office had released a public consultation document on the bill in July 2026, aiming to finalize the draft before the end of the year.
Meanwhile, the rapid expansion of AI also poses risks to financial stability.
According to the Financial Stability Report 2026, published on October 5th by the ASEAN+3 Macroeconomic Research Office (AMRO), Southeast Asian economies, along with China, Japan, and South Korea, are particularly vulnerable if the AI market experiences a sharp correction.
This is because the region holds a crucial position in the global AI supply chain and is increasingly integrated into financial markets related to this technology.
AMRO warns that an uncontrolled correction could lead to a decline in technology exports, investment losses, capital withdrawals, increased financial pressure on businesses, and a decrease in market confidence.
These warnings come amidst continued strong investment in AI. On October 8th, the World Trade Organization (WTO) raised its forecast for global merchandise trade growth in 2026 from 1.9% to 3.9%, with investment in AI infrastructure being a key driver.
According to the WTO, AI-related products such as semiconductors and servers contributed 47% to the increase in global merchandise trade value in the first half of the year, with trade volume rising 67% year-on-year.
The week’s developments show that AI is both a driving force behind investment, trade, and technological development, and a source of new challenges for cybersecurity, data protection, and financial stability. As AI becomes increasingly empowered to perform tasks autonomously, the need for security, monitoring, and accountability is becoming more critical.
An Binh